
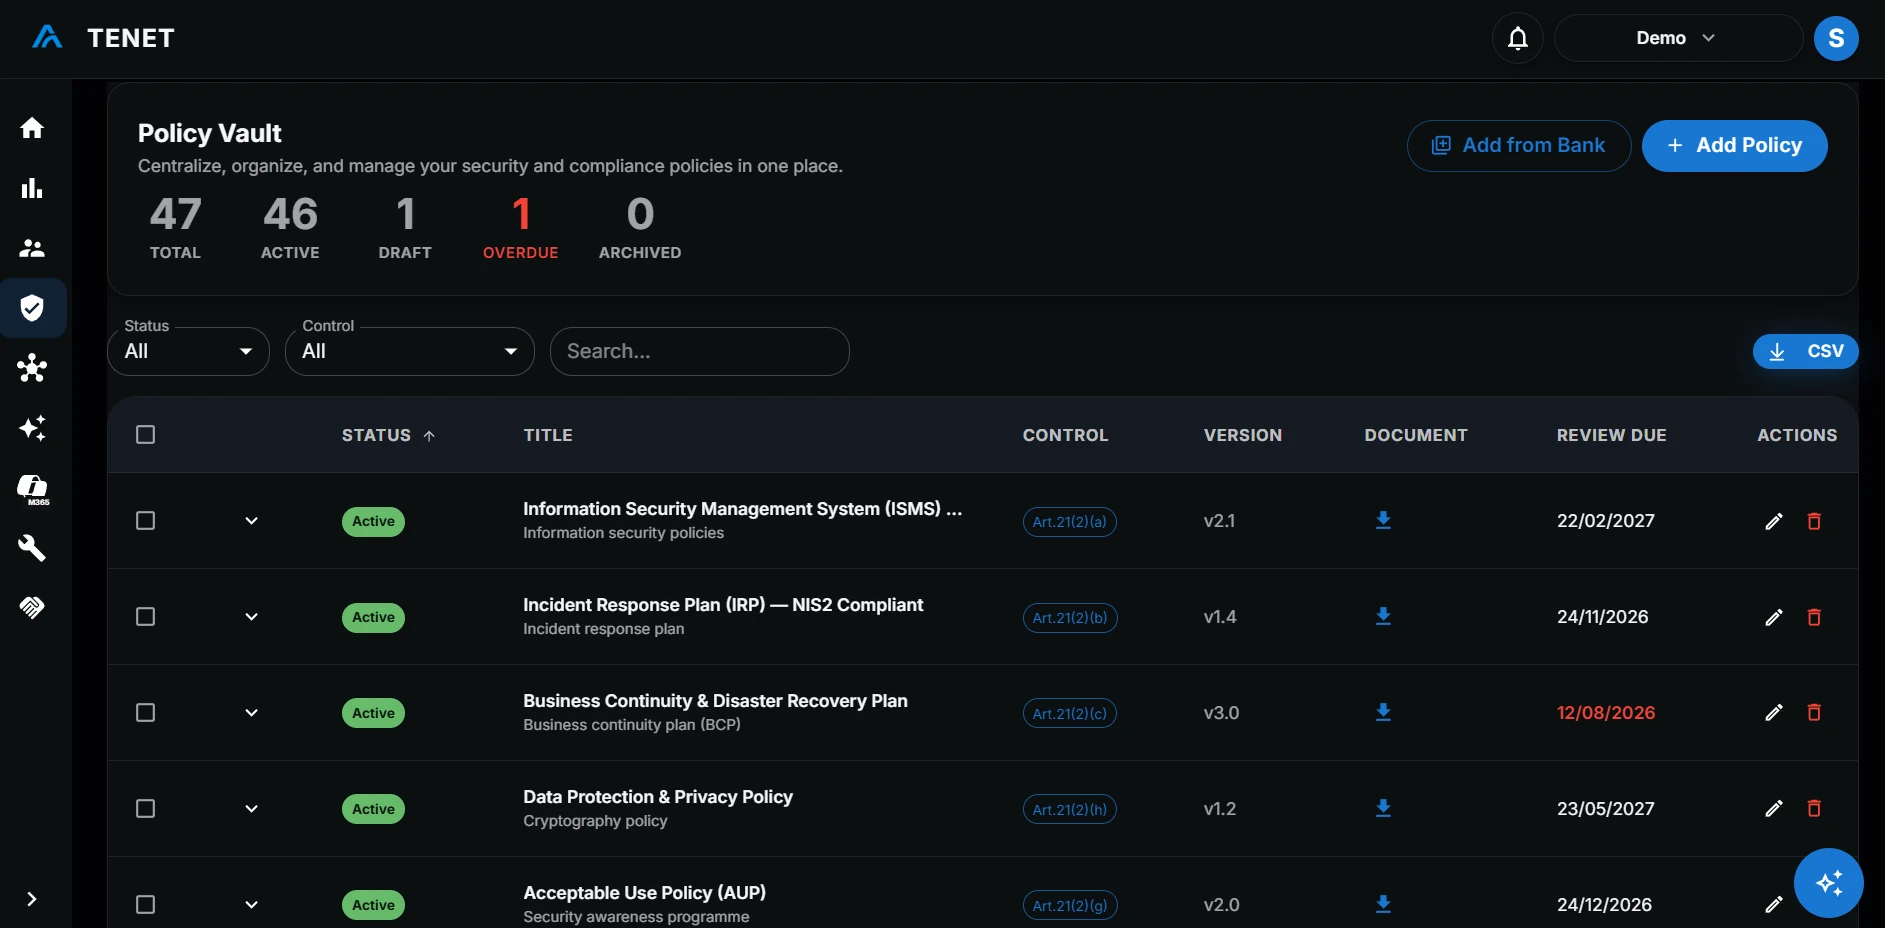
Centralized Policy Vault
Store every information security policy in one place, with a Policy Bank of ready-made templates for NIST CSF 2.0 and NIS2 Art.21. Each policy is Draft, Active or Archived, and you can attach its document.
Framework Mapping
Link each policy to the NIS2 article or NIST requirement it supports. An active policy with an attached document counts as evidence toward that requirement on the Compliance tab. Drafts do not.
Version Control
Each policy has a version number that starts at 1.0 and that you set when you edit it. The current version is shown in the Policy Vault list, so everyone can see which wording is in force.
Review Tracking
Set a review due date on each policy. Overdue policies are highlighted in red and counted in the Policy Vault header, so you can act on them before an audit.
Explore more resources
Achieve compliance the easy way.
Reduce manual work and demonstrate a commitment to cybersecurity best practices across your Microsoft cloud environment.