
BriteAI: “prod-pipeline-sp has Owner + Key Vault Admin across 3 subscriptions. Blast radius: full key exfiltration + resource takeover. Recommend scoping to least-privilege Reader + Key Vault Secrets User.”
Detect identity risks
Identify IAM misconfigurations such as over-privileged admin roles, principals without MFA, or identities with excessive permissions, with guided remediation steps to reduce access.
Spot compromised accounts
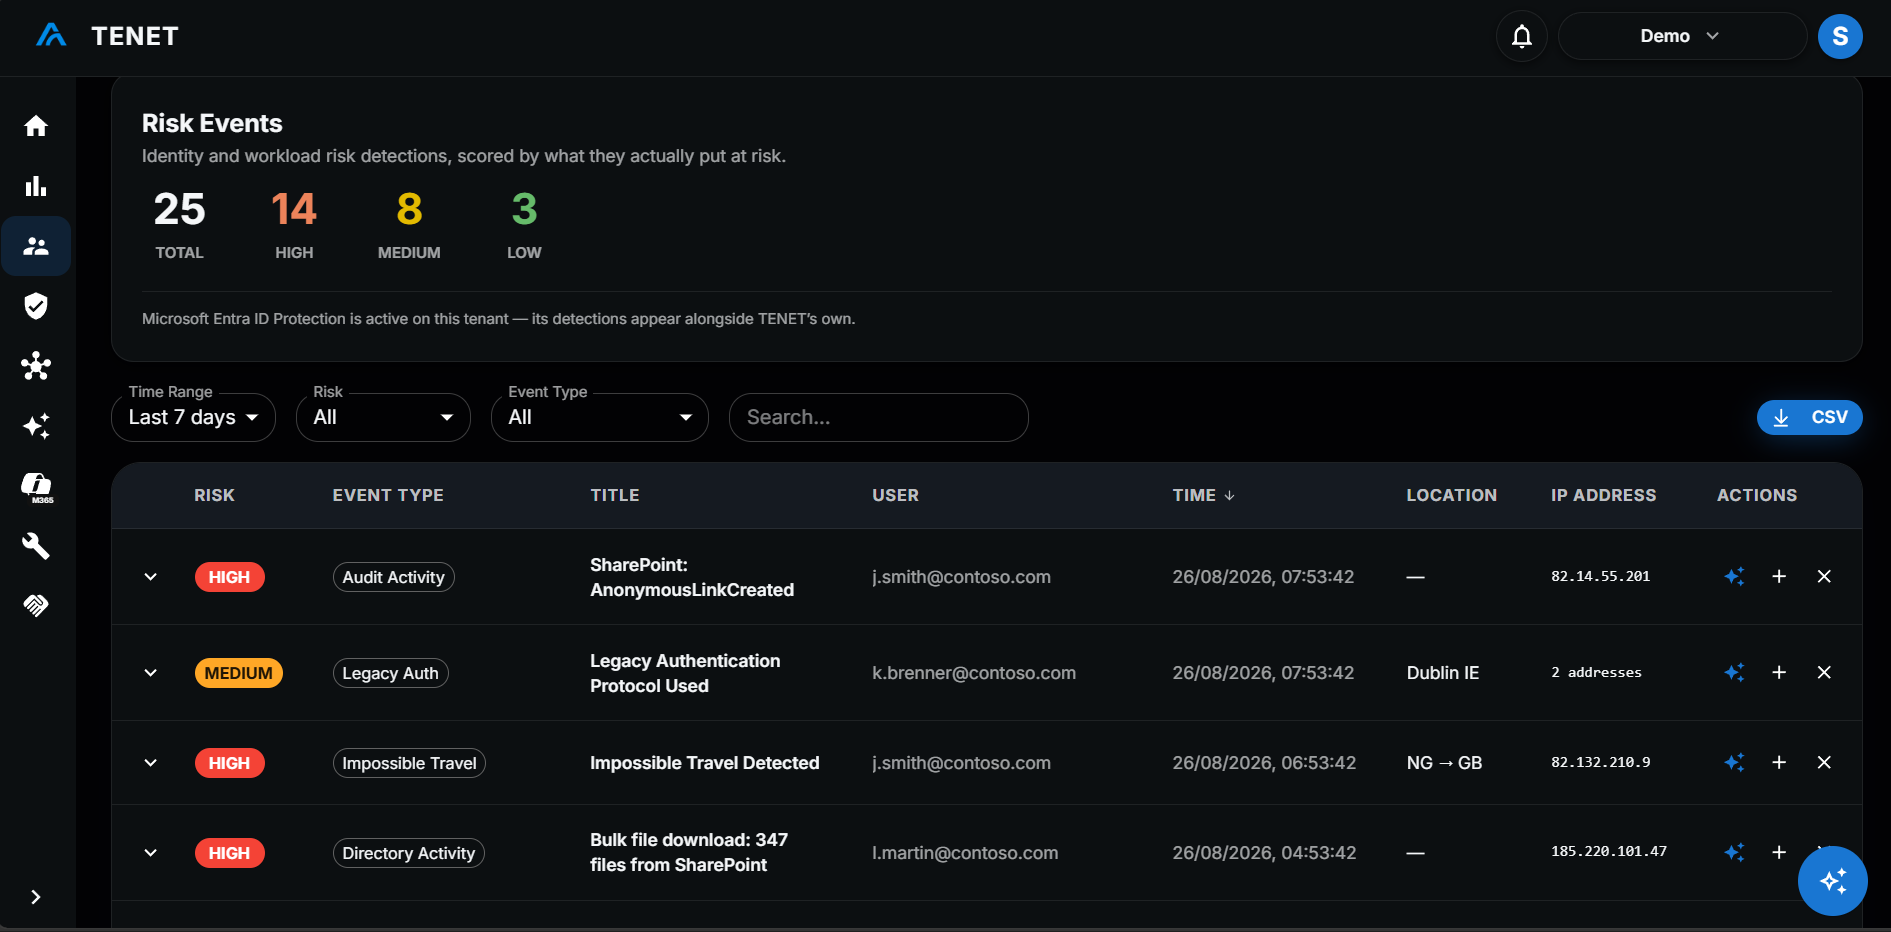
Quickly spot suspicious activity that could signal a compromised account: impossible travel, legacy authentication, bulk permission changes and suspicious consent grants. TENET's own heuristics run on Entra ID sign-in and audit logs.
admin@contoso.com signed in from United States then Singapore 22 minutes later. Physical travel is impossible: potential account takeover.
Add app role assignment to service principal · Add OAuth2PermissionGrant · Consent to application: 3 operations by svc-deploy in 4 minutes.
jdoe@contoso.com authenticated via IMAP4. Legacy protocols bypass Conditional Access and MFA: credential spray target.
Every identity risk event TENET detects
Detected from Microsoft Entra ID sign-in and directory audit logs (via Microsoft Graph), Microsoft 365's collaboration audit log, and Entra ID Protection risk scoring where licensed. Sign-in detections need Entra ID P1.
Impossible travel
A sign-in pattern implying physically impossible movement between locations.
Risky and anomalous sign-ins
Leverages Microsoft's own Entra ID Protection risk scoring where the tenant is licensed for it.
Legacy authentication use
Sign-ins using older protocols that bypass modern MFA controls.
Credential attacks
Password spray and brute-force patterns detected across accounts.
Bulk directory operations
An unusual volume of account or permission changes by one admin, baselined against their own normal activity.
Privilege and consent changes
Role grants and app consent grants, scored by what was actually granted: a tenant-wide grant of a sensitive permission ranks higher than a narrow one.
Suspicious AI agent identity sign-ins
The same sign-in detection applied to AI agent identities, not just human accounts.
Correlated multi-signal incidents
Several of the above happening to the same account in a short window: flagged as a likely account takeover.
Unfamiliar sign-in properties
A successful sign-in from a country, network, browser or device the account has not used before, judged against its own history.
Unusual administrative actions
A privileged operation an administrator has never performed before, judged against their own recent activity.
Applications flagged by Microsoft
Apps in your tenant that Microsoft has disabled or flagged for violating its terms, so you can review and revoke what they were given.
External sharing and mail-flow changes
Anyone links, files shared outside the organization, and mailbox rules that forward or hide mail, scored by what the record actually shows.
BriteAI-Guided Response
Ask Brite on any risk event to see what it means, its likely cause and what to investigate next. Add to Remediation turns it into a tracked task. Accept risk dims events you have reviewed.
Explore more resources
Take control of your identity risks
Get started with Identity Security reimagined today.
14-day free trial · No credit card required · Cancel anytime