
Detect identity risks
Identify IAM misconfigurations such as principals without MFA, or identities with excessive permissions, and surface risky identities and suspicious user activity so you can catch account compromise early.
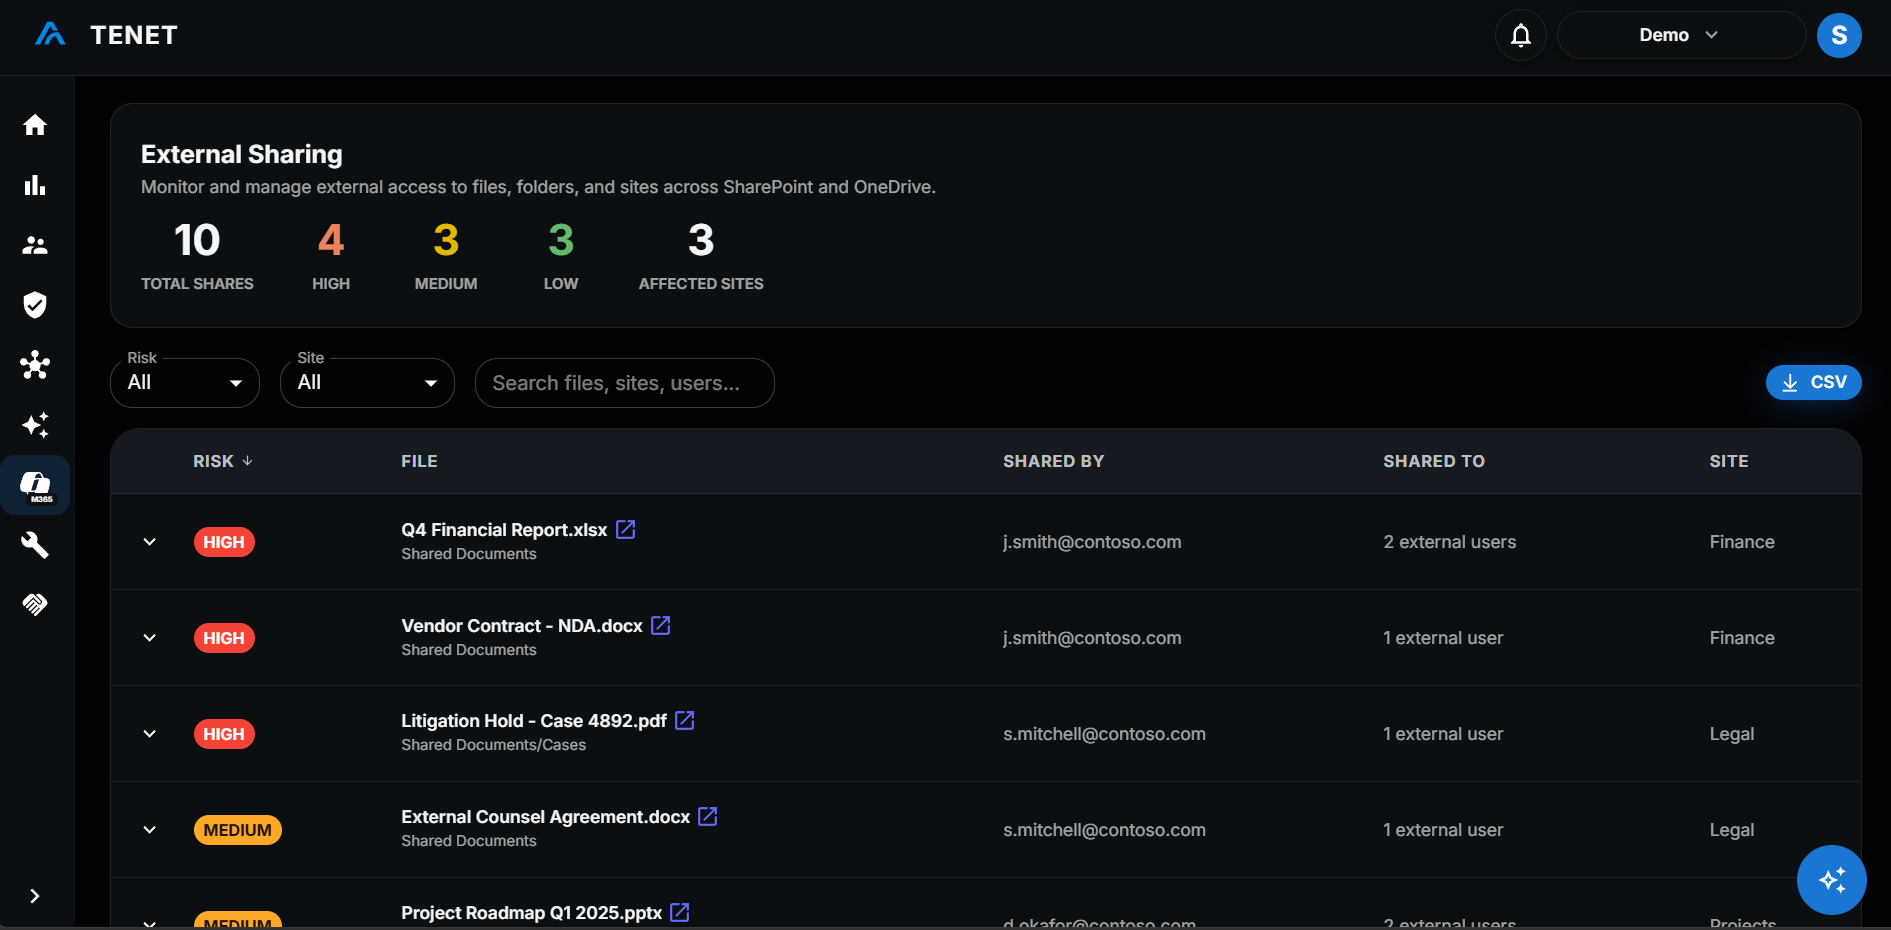
External data access
Track external sharing across SharePoint and OneDrive. Identify files and folders exposed to external users or anonymous links and reduce data exposure before it becomes a breach. Filter by risk, site or recipient and export to CSV.
Compliance monitoring
Automatically map your M365 security controls to compliance frameworks. Identify misconfigurations prioritized by risk, track remediation progress, maintain audit evidence and generate executive-ready reports.
Govern application access
Discover every third-party app and OAuth permission grant in your tenant. TENET surfaces overprivileged or untrusted apps, and lets you mark each one Approved or Needs Review and assign review tasks, all from one view.
Unified incident context
See Microsoft Sentinel and Microsoft 365 Defender incidents with unified cloud context. Use BriteAI to investigate root cause, and correlate them with identity, device and workload risks already tracked in TENET.
Endpoint Exposure Risk
Correlate Intune device status, Defender for Endpoint findings with TENET's security graph to identify risky entry points such as software or OS vulnerabilities and map likely attack paths and toxic combinations across your estate.
Explore more resources
One view of cloud risk
Use TENET to monitor, prioritize, and remediate risk across your Microsoft estate from one operational platform.