
Reduce AI Attack Surface
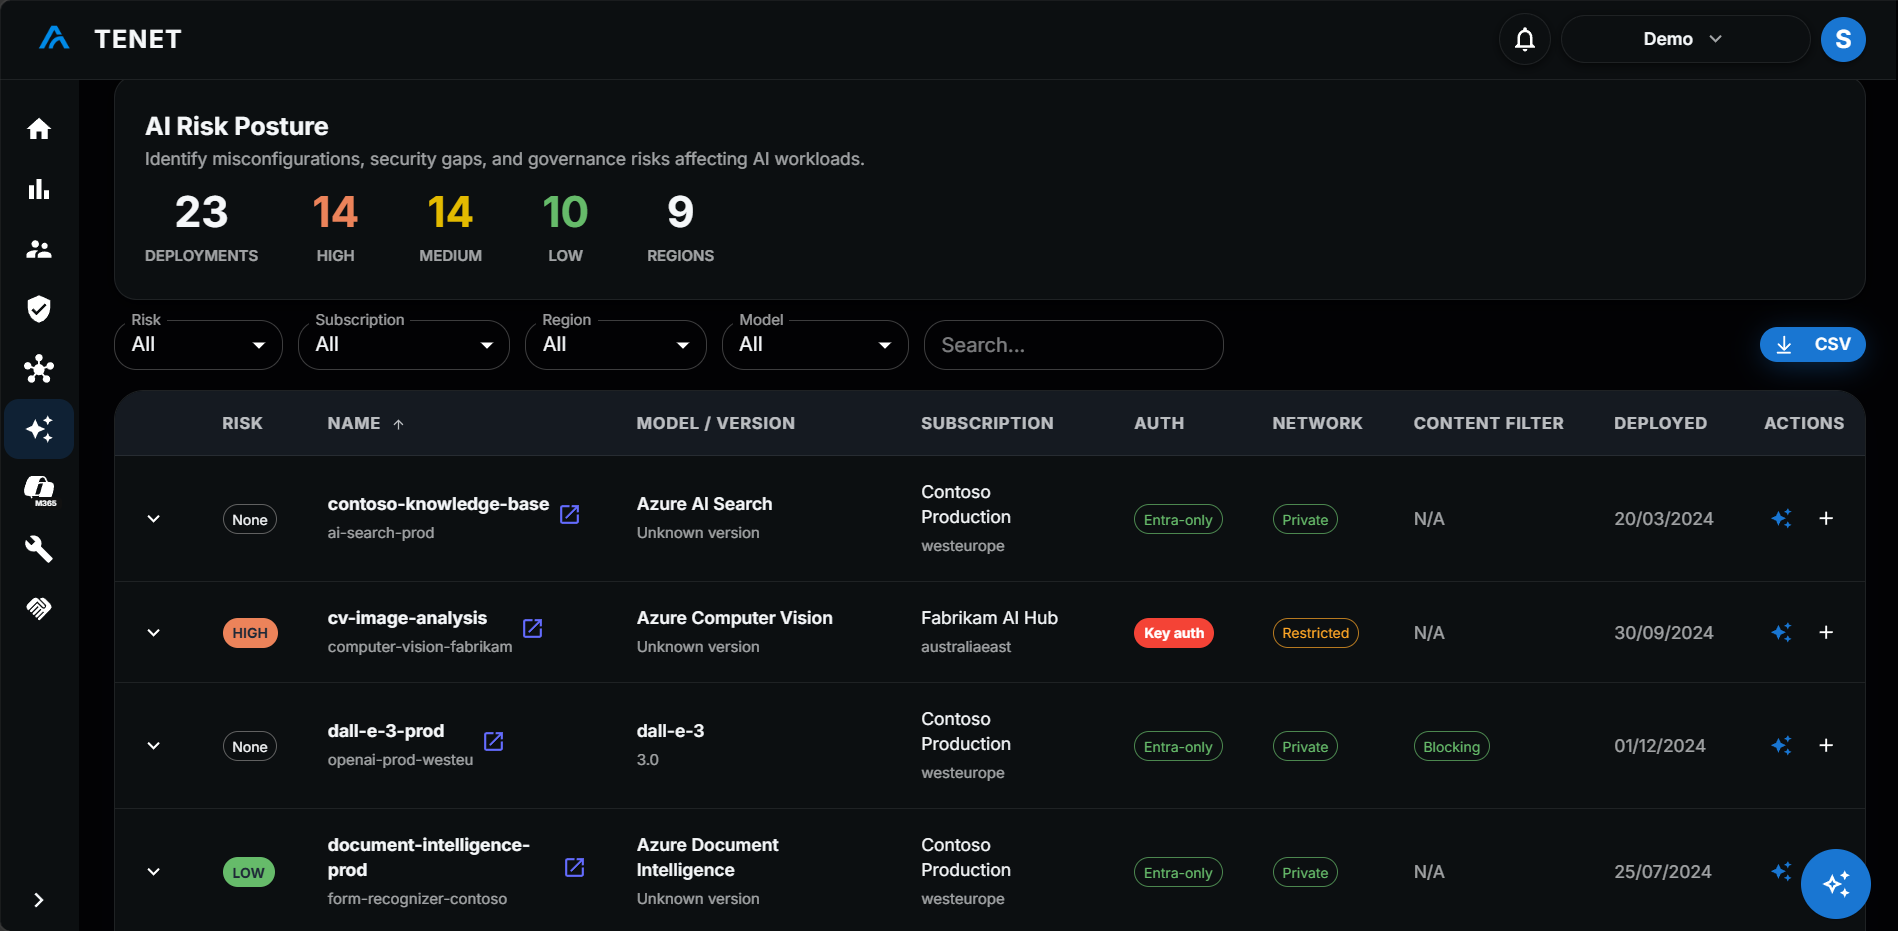
Identify AI-native risks and publicly exposed endpoints to uncover misconfigurations and close exposure before attackers target them.
Audit content filter policies
See which deployments have content filter policies configured and track aggregate blocked requests. Identify unprotected deployments that may return unfiltered outputs in production.
End-to-end configuration guardrails
Beyond network exposure, authentication, and content filtering, TENET checks four more configuration-level guardrails on every Azure AI resource.
Quota pressure
Flag deployments running close to their token or request quota, since capacity pressure is itself a posture risk.
Encryption and key management
Audit key management settings on AI resources, including whether keys are customer-managed or platform-managed.
Audit logging
Flag Azure AI resources with no diagnostic settings, so their activity is not routed anywhere for review.
Model lifecycle
Warn when deployed models are deprecated or approaching end of life, before they stop working.
Guided Hardening
Each posture finding can become a tracked remediation task, pre-filled with the affected resource and details. Ask Brite for remediation steps or Azure CLI commands for any finding.
Secure and optimize AI workloads
Get complete visibility across your Azure AI stack from day one and reduce AI risk with a single platform.