Identity & Access Management

Secure Identities (CIEM)

Discover human and non-human identities and their entitlements across your environment, then identify excessive access and risky permission reach.

START FOR FREEREQUEST DEMO
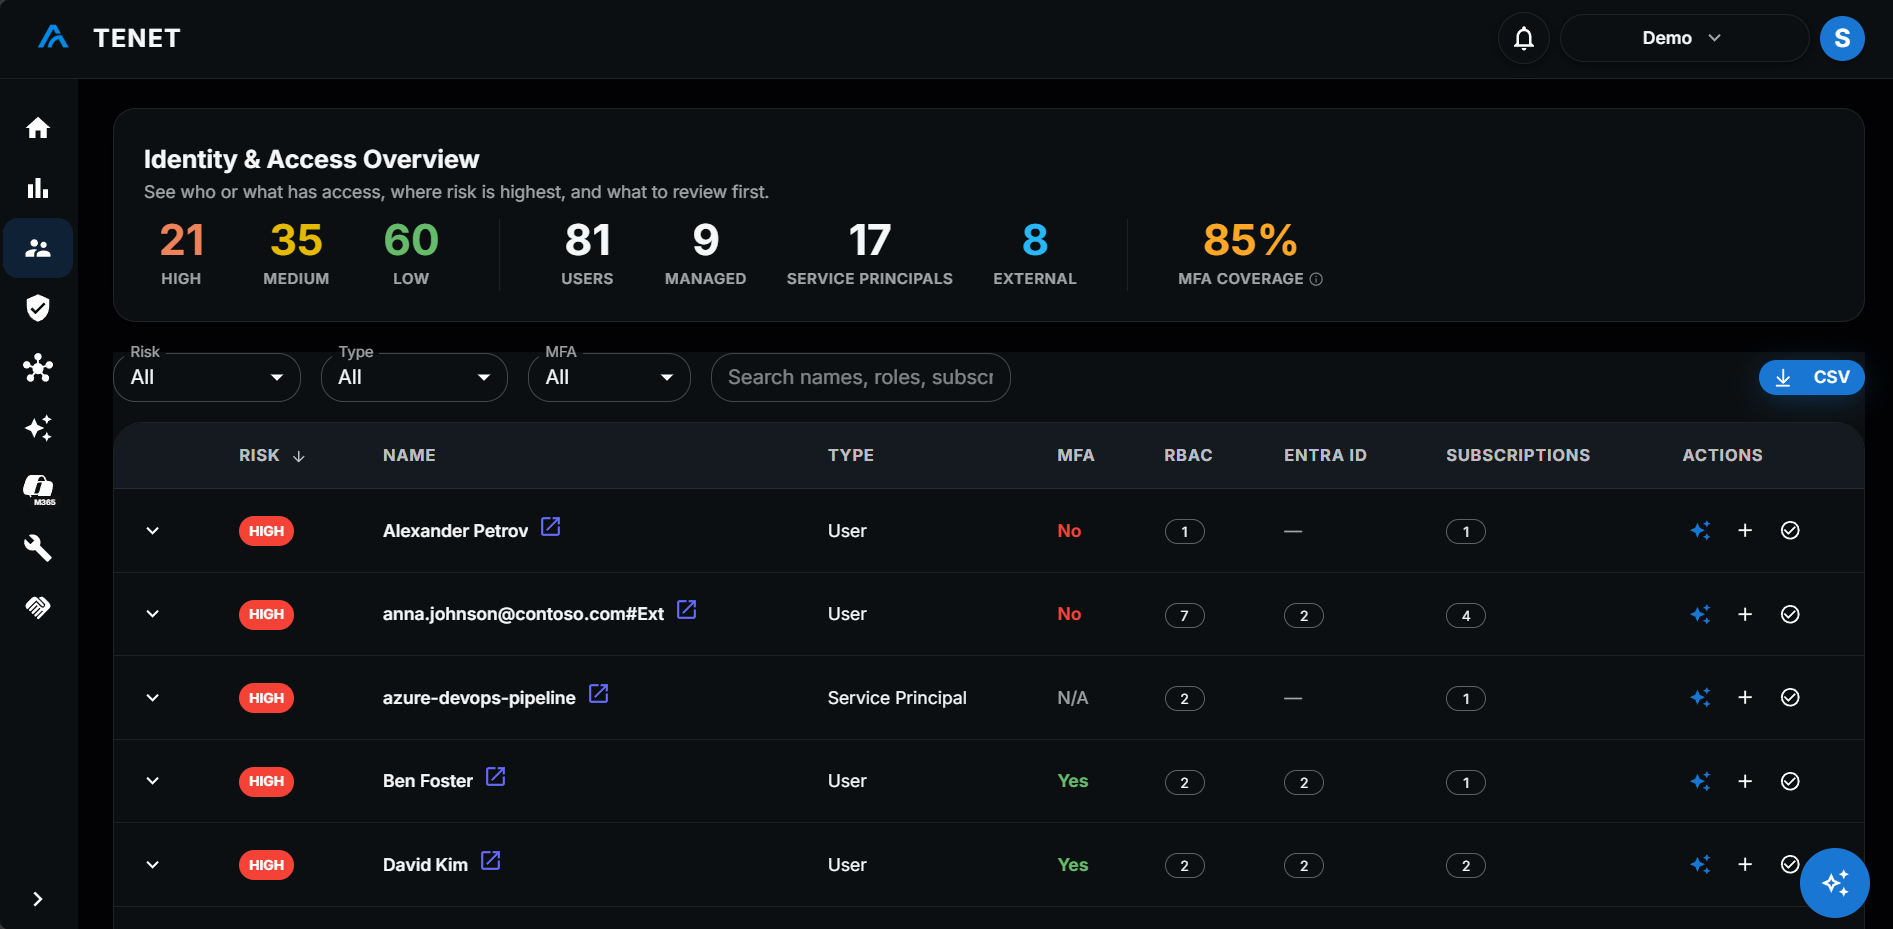
TENET Identity and Access Overview listing users and service principals with risk level, MFA status and role assignments
Identity Discovery: Environment Overview
Users
248
Human Identities
Service Principals
61
App Registrations & SPs
Managed Identities
28
System & User Assigned
Groups
34
Entra ID Groups
42 identities with excessive permissions
Recommend least-privilege scoping
High
13 identities with Owner or Contributor
Broad roles held across subscriptions
High
8 accounts with no MFA enforced
Privileged users missing MFA requirement
Medium
Identity Discovery

Discover identities and entitlements

Discover and inventory human and non-human identities and their entitlements. Track permissions to reduce the risk of excessive access. See each user's MFA status, and accept a risk once your team has reviewed it.

Service Principal Governance

Secure non-human identities

Analyze service principals and managed identities, assess their access across your environment, and detect identity risks in a single unified platform.

Service Principal Inventory
Managed Identities
28
System & User Assigned
Service Principals
14
App Registrations & SPs
High Risk
6
Broad or privileged access
Medium Risk
11
Elevated or scoped access
prod-pipeline-sp has excessive permissions
Owner + Key Vault Admin across 3 subscriptions
High
2 service principals with subscription-wide roles
Scope could be narrowed to a resource group
High
5 managed identities with elevated roles
User Access Administrator on 3 subscriptions
Medium
Role assignments
svc-reporting
Owner · Subscription scope
Over-privileged
Finance team
Reader · Resource group scope
Excessive access

Excessive Access Detection

Role assignments are listed with their scope, and over-privileged assignments are highlighted, such as the Owner role at subscription scope.

Least privilege

Least-Privilege Guidance

Ask Brite on any identity to see why its risk level was set, with suggested steps such as removing excessive permissions or reducing scope.

Identity · svc-reporting
Suggested steps
1. Remove the Owner role
2. Reduce scope to the resource group it uses
Ask BriteAdd to Remediation

Take control of your identity risks

Get started with Identity Security reimagined today.

FREE ASSESSMENTREQUEST DEMO

14-day free trial · No credit card required · Cancel anytime