Attack Surface Management

Third-Party App Risk

Detect unknown apps, risky third-party access, and excessive permissions across your environment, and track which apps your team has reviewed.

START FOR FREEREQUEST DEMO
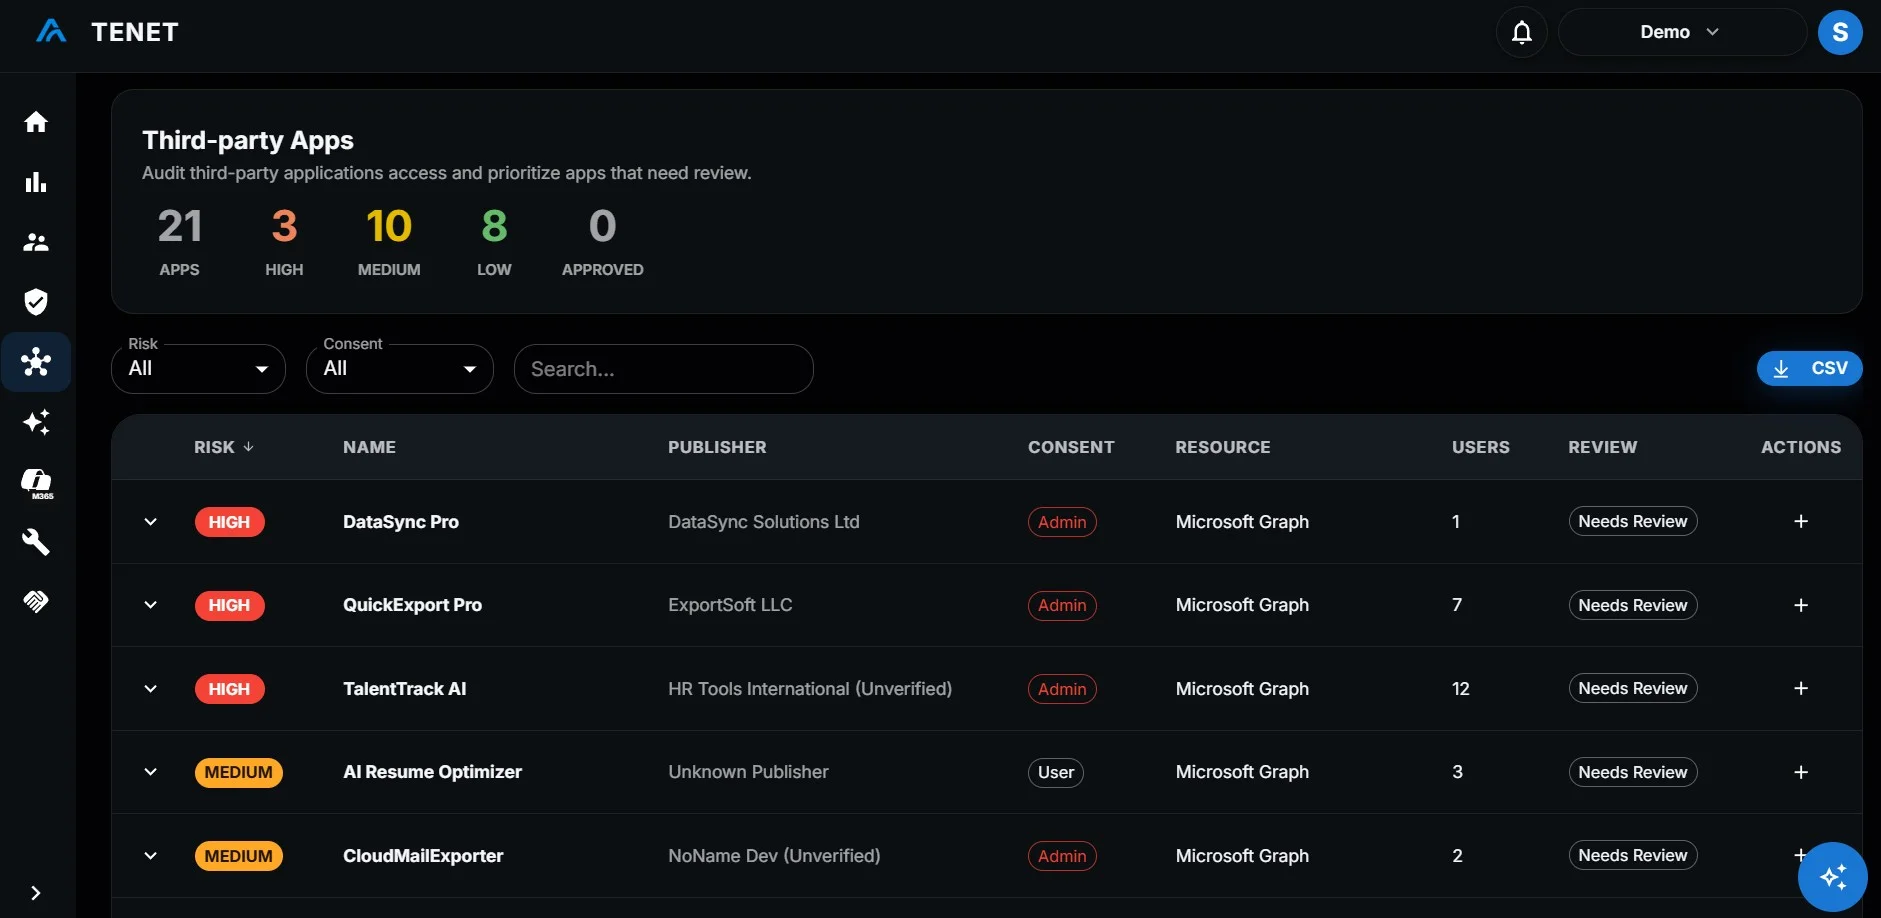
TENET Third-party Apps view listing apps by risk, publisher, consent type, resource and number of users
Third-Party Apps
xhr-sync-worker-v2High
Mail.Read · Files.ReadWrite.All
Consent: User
o365-ext-connectorHigh
Mail.ReadWrite · Mail.Send
Consent: User
plugin-bridge-svcMedium
User.ReadBasic.All · openid
Consent: User
data-sync-helper-3xMedium
Calendars.ReadWrite · Contacts.RW
Consent: User
Third-Party App Discovery

Uncover unapproved apps

Detect shadow IT and bring unknown apps and risky third-party access into view. Identify unsanctioned apps and excessive permissions, including whether each came from admin or user consent, before they become exploitable.

Permission scopes

Excessive Scope Detection

Each app's requested permission scopes are shown as tags: red for high-risk, amber for medium-risk. Its risk level reflects scope sensitivity and whether consent is tenant-wide.

Permission scopes · xhr-sync-worker-v2
Files.ReadWrite.AllMail.ReadUser.Read
Consent: Admin (tenant-wide) · Risk level: High
App review
data-sync-helper-3x
Approved by IT Security · 12 Aug 2026
Approved
plugin-bridge-svc
Not yet assessed
Needs Review
Review

Review Workflow

Each app stays Needs Review until your team approves it. Approving records who approved it and when, so anyone can see the app has already been reviewed.

Remediation Tracker

Turn findings into action

Move from insight to closure faster with clear, prioritized fixes. Convert every security gap into a tracked, assigned task with priority, owner, and due date, giving your team a clear path from discovery to resolution.

Remediation
vm-compute-eastus-4: block inbound RDP from 0.0.0.0/0In Progress
Entry node in 3-hop path · T1190 · Score 91
Attack PathPriority: CriticalOwner: a.patelDue: Today
bg-task-runner-0041: revoke Directory.ReadWrite.AllOpen
Admin-consented · unrecognized publisher · permission never observed in use
M365 AppPriority: CriticalOwner: j.mooreDue: Apr 23
svc-identity-prod: reduce Owner assignments to 3 subscriptionsOpen
Pivot node · managed identity used in active attack path · T1078
Attack PathPriority: HighOwner: s.chenDue: Apr 25
storage-files-01: restrict SMB port 445 to corp IP rangeResolved
Open to 0.0.0.0/0 · reachable from attack path target subnet
Port ScanPriority: HighOwner: s.chenDue: Apr 27

Visibility that reduces risk

Get a complete picture of your risk, with insights and prioritised actions that take your team from finding to fix.

FREE ASSESSMENTREQUEST DEMO