NIS2 Compliance

NIS2 compliance
for Microsoft cloud

Take a proactive, risk-based approach to NIS2 with a unified platform that replaces fragmented processes, strengthens resilience, improves visibility, and simplifies compliance assurance.

START FOR FREEREQUEST DEMO

14-day free trial · 2 min setup · No credit card required

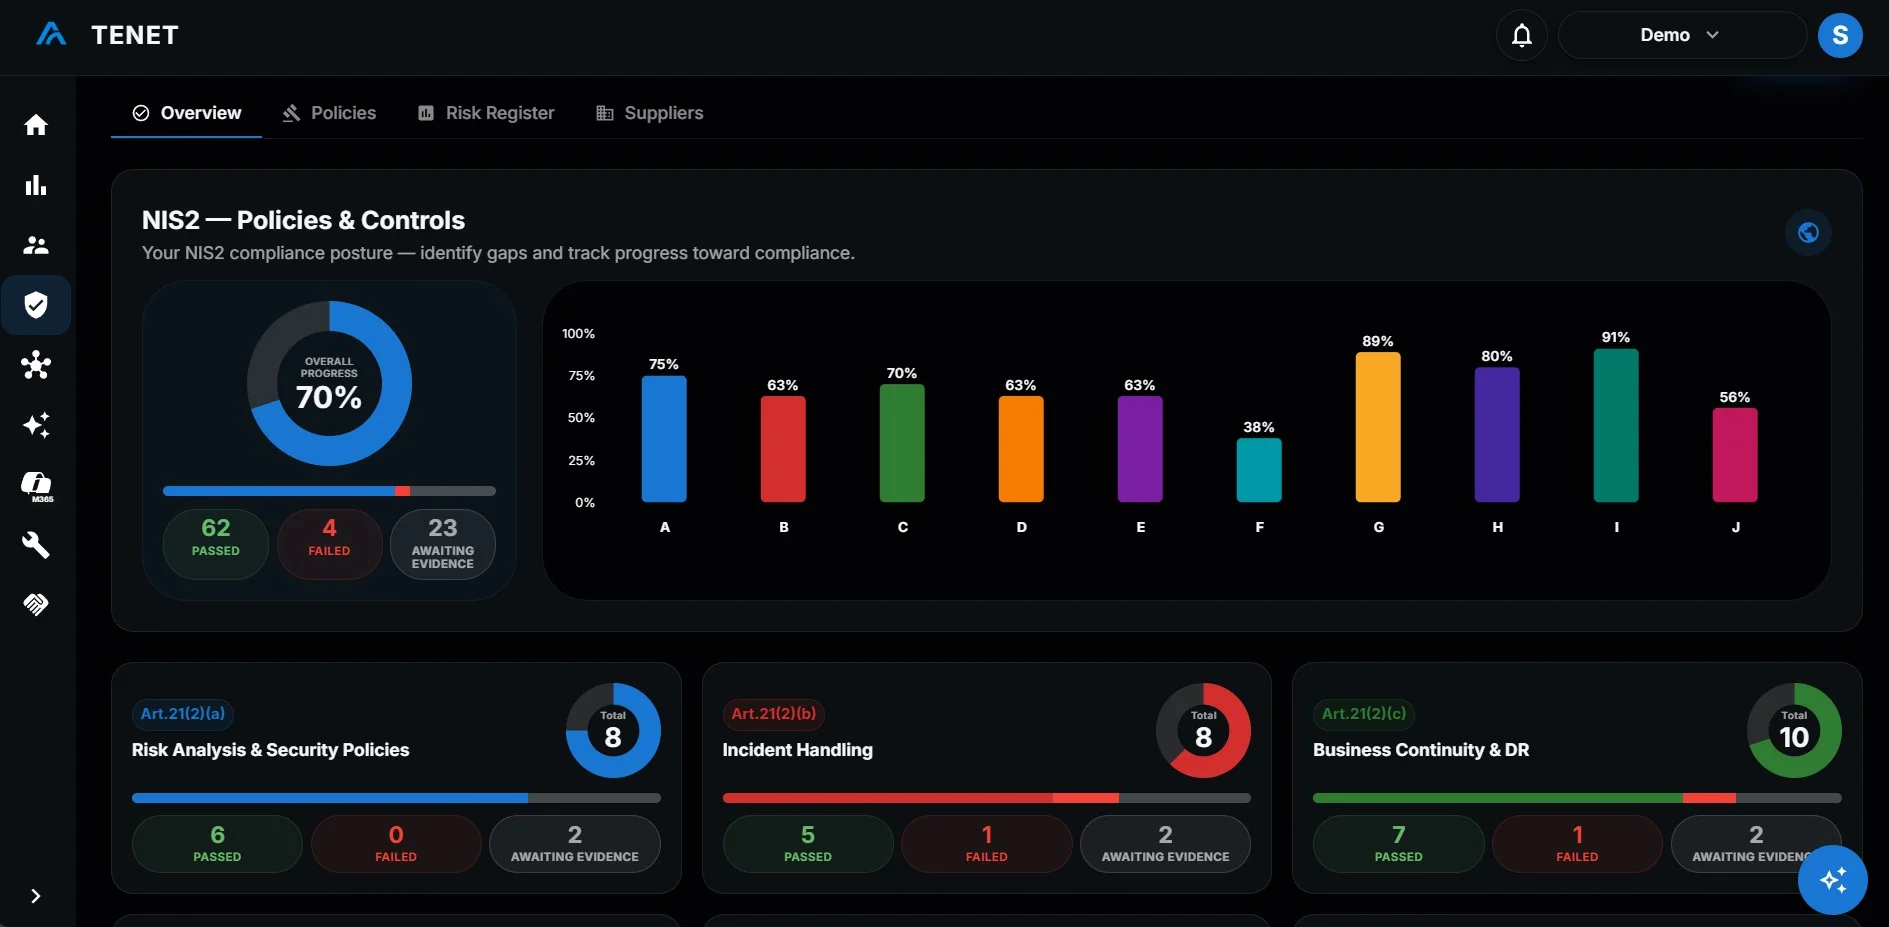
TENET dashboard showing NIS2 compliance progress across the Art.21(2) security measures
Who It Is For

Who is NIS2 for?

Essential EntitiesAnnex I

Larger organisations in critical sectors

Energy providersTransport operatorsFinancial institutionsHealth sectorDrinking waterWastewaterDigital infrastructureICT service managementPublic administrationSpace
Important EntitiesAnnex II

Mid-size organisations in additional sectors

Postal & courier servicesWaste managementChemicalsFood productionManufacturingDigital providersResearch organisations
Compliance Intelligence

Built-in compliance intelligence

Detect compliance drift, generate reports, and monitor NIS2 posture through automated assessments across your Azure and Microsoft 365 environments.

Simplify investigation

Drill down into the NIS2 framework to its associated categories, all the way down to controls and resource-level assessments across your Azure and Microsoft 365 environment. Questionnaires open with ENISA-based guidance on what good looks like, Microsoft 365 controls are grouped by Identity, Data, Apps and Device, and a toggle switches the same view to NIST CSF 2.0.

Compliance Drift Detection

Detect compliance drift on every refresh, not weeks later during a periodic review. TENET re-assesses your controls automatically so your posture stays current and audit-ready.

Risk-Based Prioritisation

Surface the misconfigurations that carry the most compliance risk, ranked by control severity, so your team focuses remediation where it matters most.

NIS2 Requirements

What does NIS2 require?

Identifying whether your organisation qualifies as an essential or important entity
Implementing comprehensive cybersecurity risk management measures
Establishing incident detection, response, and reporting processes
Securing supply chains and managing third party risk
Ensuring senior leadership accountability and governance oversight
Maintaining ongoing monitoring, testing, and continuous improvement
Business Benefits

Benefits of achieving NIS2 compliance

Operational resilience
Protect your critical cloud infrastructure and ensure continuity in the face of evolving cyber threats.
Reduced regulatory and financial risk
Meet mandatory requirements and avoid penalties through structured, defensible compliance.
Improve visibility and control across your organisation
Gain a clear understanding of risk and policy effectiveness so no threat goes undetected.
Build trust with partners, and customers
Demonstrate a proactive approach to cybersecurity and resilience.
Strengthen supply chain resilience
Address NIS2 Art.21(2)(d) by bringing third-party risk into the same platform as your compliance posture: not a separate spreadsheet.
Compliance posture

Reduce compliance friction

Automated scoring across the NIS2 framework marks a requirement met when its mapped controls pass or its evidence is filed. Download the compliance report for auditors and focus remediation on the highest risks.
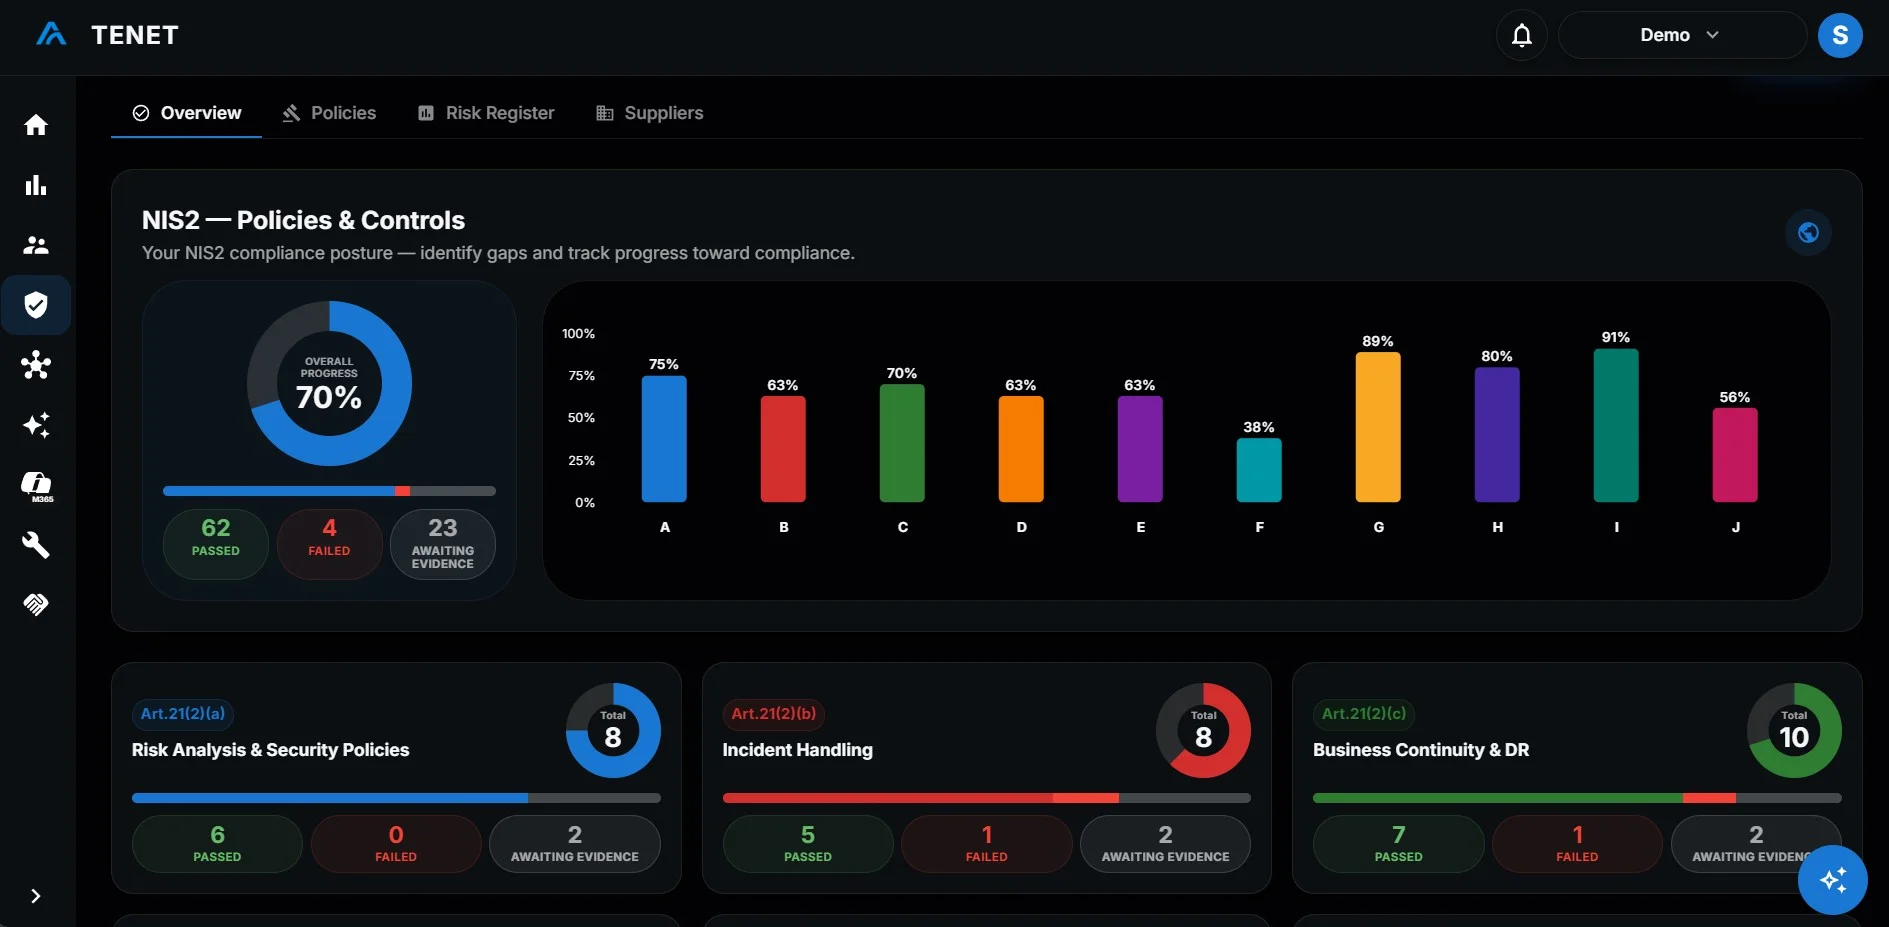
TENET NIS2 compliance posture dashboard
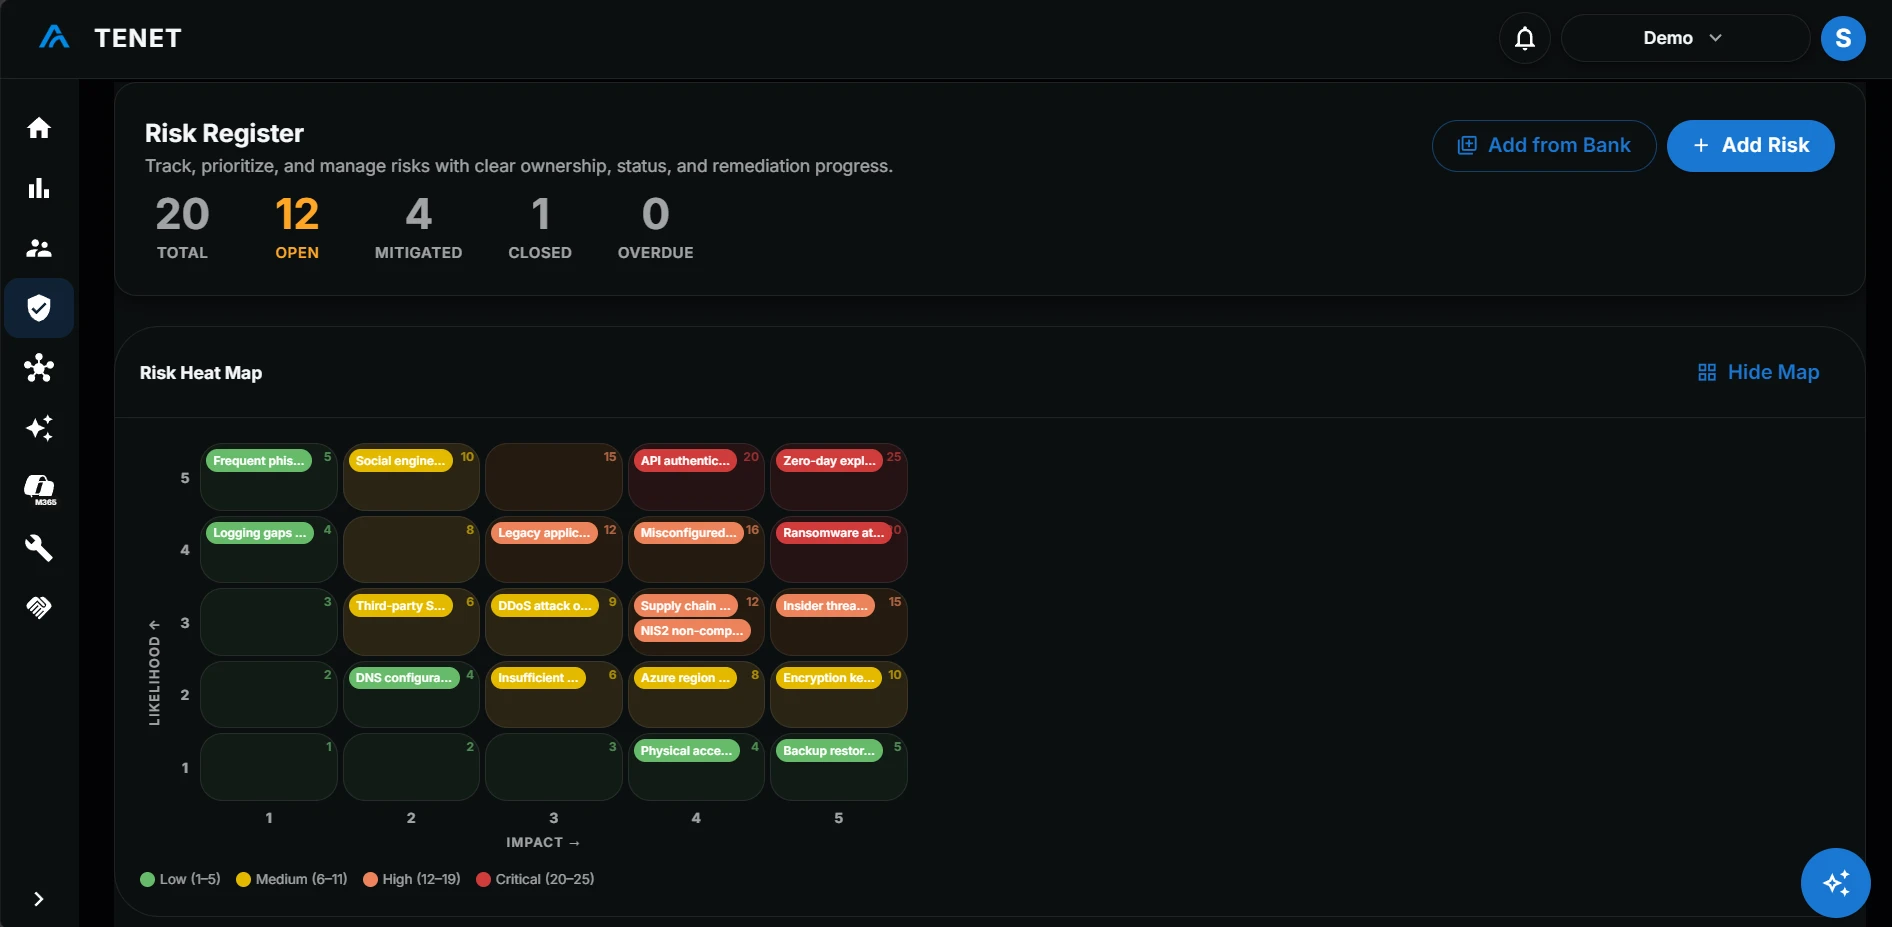
TENET risk register heatmap
Risk management

Catalogue and manage business risk

Create, catalogue and visualise business risks in one place, starting from pre-built risk templates. Record clear assessment, ownership and treatment rationale to document your risk analysis for compliance auditors.

LEARN MORE
Audit evidence

Policy management

Store, version and manage your information security policies in one place, starting from ready-made templates. An active policy filed against a requirement counts as evidence toward it.

LEARN MORE
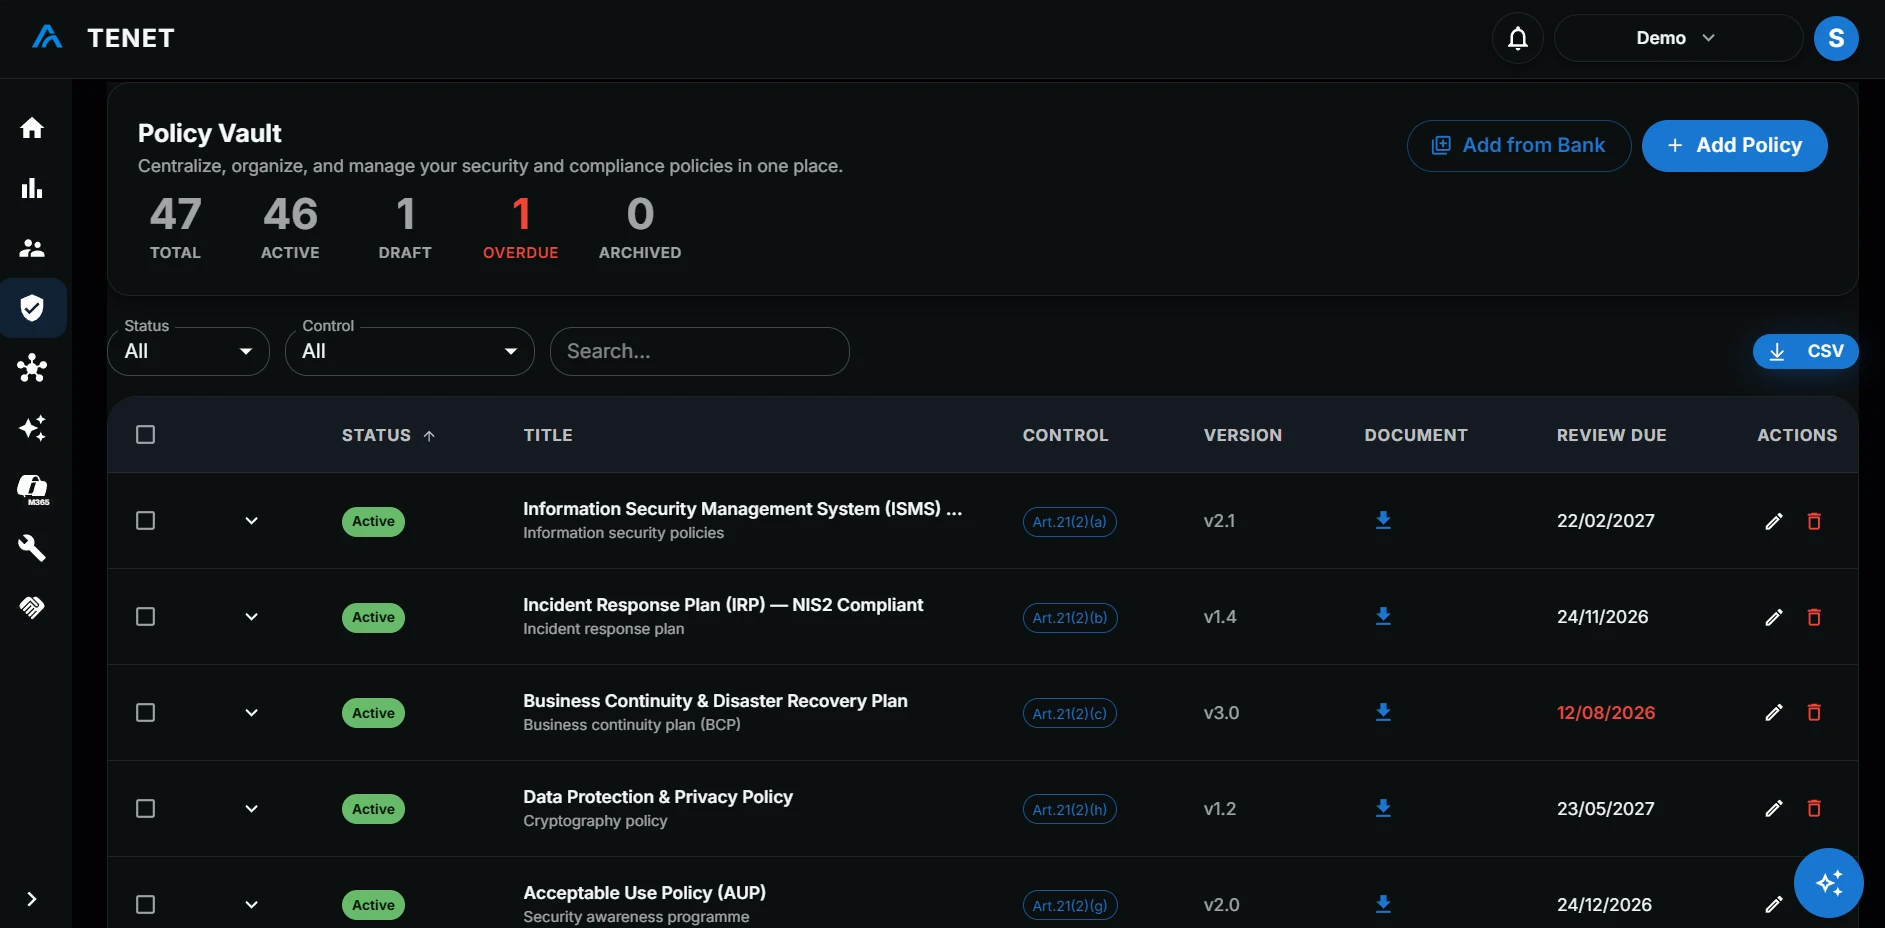
TENET NIS2 policies mapped to controls
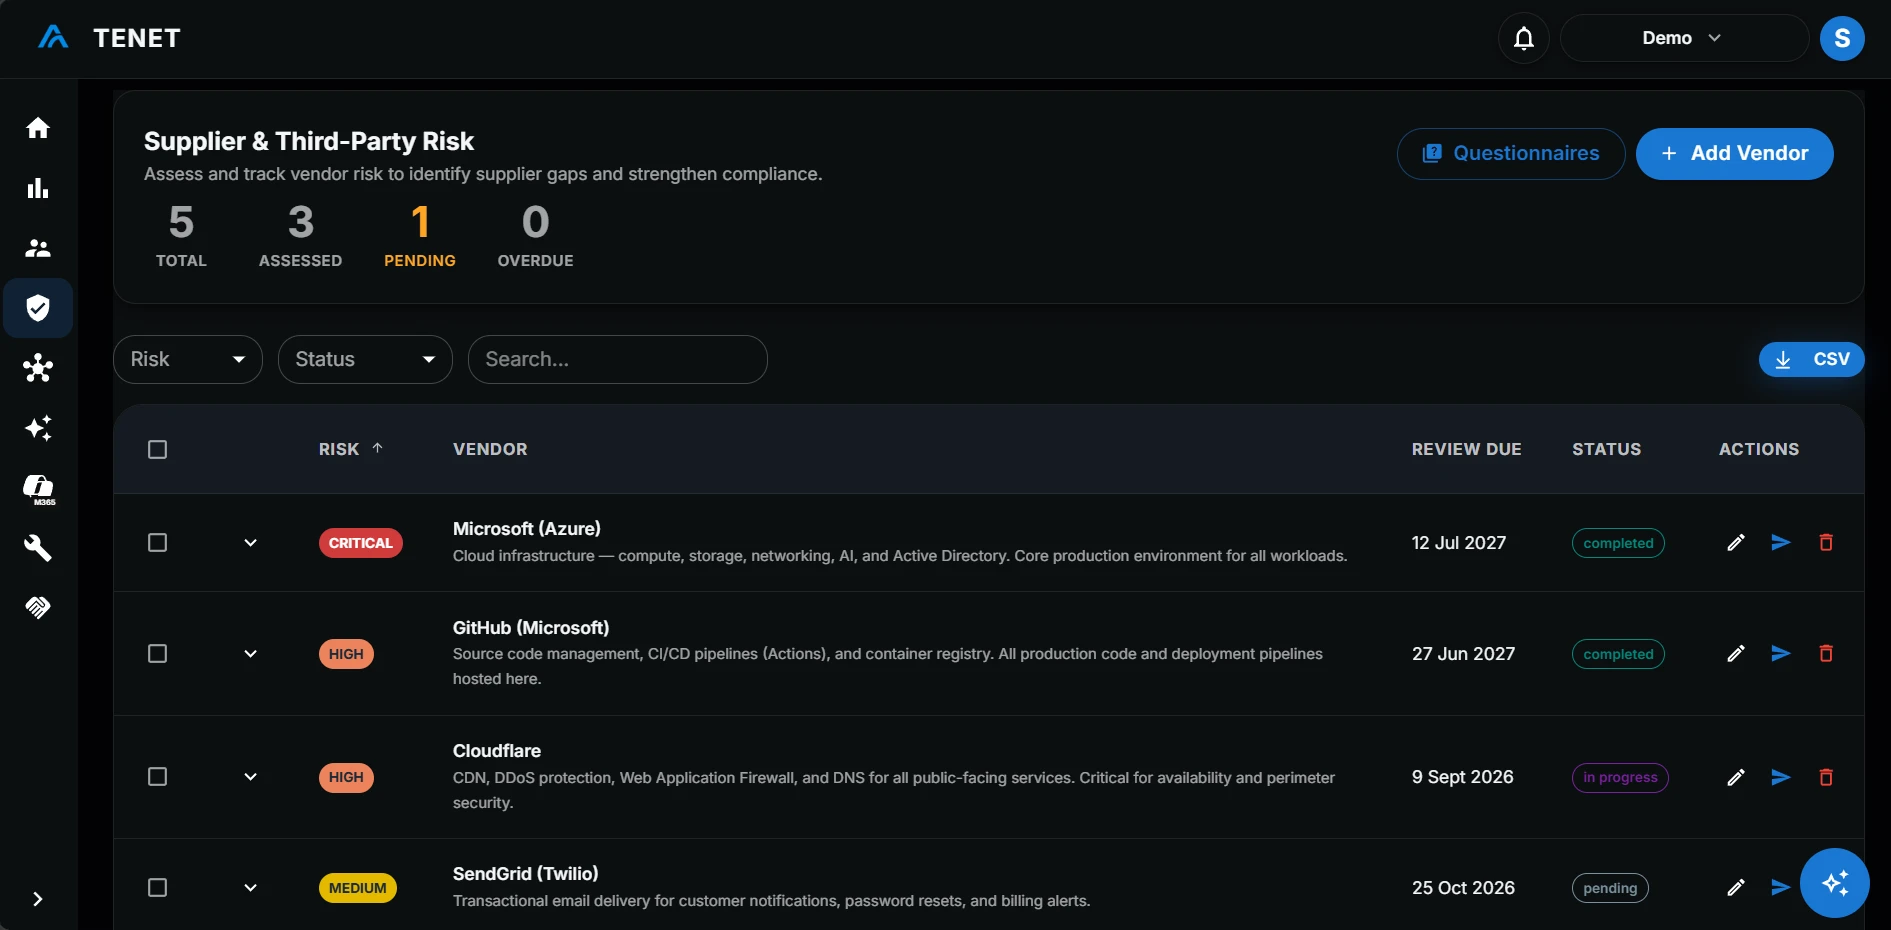
TENET NIS2 supplier management
Supply chain risk

Integrated vendor risk management

Supply chain risk is a growing focus under NIS2, and managing it manually quickly becomes unsustainable. Maintain your ICT supplier inventory, integrate supply chain risk into your compliance posture, and use questionnaires.

LEARN MORE
Workflows

Every compliance workflow in one place

Beyond framework dashboards, TENET ships a full suite of compliance modules that keep your programme complete and audit-ready.

Incident Handling Readiness

Cover the incident-handling requirements, including classification and the Art.23 early-warning and final-report procedures, with guided questionnaires and policy evidence.

Accelerated Remediation

Reduce mean time to remediation with a unified platform that enables teams to assign issues with remediation guidance to the right owners, and progress tracking until resolution without ever leaving the platform.

Exec-Ready Reports

Generate on-demand compliance reports that translate technical posture data into clear summaries your leadership and board can act on, in multiple languages and with no slide-deck assembly required.

How TENET Helps

Achieve and maintain NIS2 compliance

TENET gives a clear, structured approach to NIS2 requirements, helping you strengthen operational resilience, manage cloud risk and demonstrate compliance. Move from reactive controls to an always-current posture.

Meeting NIS2 requirements is not just about implementing controls. It is about ensuring your organisation can prevent, withstand, and respond to cyber threats while maintaining critical services.

Why customers choose TENET
A clear, defensible approach to NIS2 compliance
Understand your obligations, map scope, and implement controls in a structured way that aligns with regulatory expectations.
Continuous monitoring of cloud risk and resilience
Up-to-date visibility into threats, security gaps, and control effectiveness across your Microsoft cloud environment.
Built-in incident readiness
Meet incident-handling and reporting requirements with guided procedures and policy evidence, including the Art.23 timelines, tracked in your NIS2 questionnaires.
Leadership accountability and reporting
Enable senior stakeholders to take ownership of cybersecurity through structured reporting, oversight, and audit trails that demonstrate continuous compliance.

FAQs

Does NIS2 apply to my organisation?
NIS2 applies to medium and large organisations that operate in one of the in-scope sectors, either as essential or important entities. A medium organisation is defined as one with more than 50 employees or an annual turnover or balance sheet above €10M. Some organisations (such as critical infrastructure providers and top-level domain registries) are in scope regardless of size. If your organisation provides services across EU member states in an in-scope sector, you should assume NIS2 applies.
What security measures does NIS2 require us to implement?
Art.21(2) defines 10 mandatory security measure categories: risk analysis and information system security policies, incident handling, business continuity and crisis management, supply chain security, security in systems acquisition, development and maintenance (including vulnerability handling), policies to assess the effectiveness of your measures, cyber hygiene and training, cryptography and encryption, HR security, access control and asset management, and multi-factor authentication. Each category must be addressed with proportionate technical and organisational measures based on your risk exposure.
What are the penalties for NIS2 non-compliance?
For essential entities, national authorities can impose administrative fines of up to €10 million or 2% of total worldwide annual turnover, whichever is higher. For important entities, the ceiling is €7 million or 1.4% of worldwide annual turnover. Beyond financial penalties, authorities can mandate public disclosure of non-compliance findings and, for essential entities, temporarily ban individuals in management positions.
How quickly do we need to report incidents under NIS2?
Art.23 sets three mandatory reporting deadlines. Within 24 hours of becoming aware of a significant incident, you must submit an early warning to the relevant national authority. Within 72 hours, you must submit a full incident notification including an initial assessment of its severity. Finally, within one month of the incident notification, you must submit a final report covering the full description, impact, root cause, and any cross-border implications. TENET helps you prepare by tracking the incident-handling and reporting procedures behind each deadline as part of your Art.21(2)(b) requirements.
How does TENET simplify NIS2 compliance?

TENET simplifies NIS2 compliance by automating the mapping of your security controls and evidence to the NIS2 requirements. It provides continuously refreshed compliance monitoring, automated reporting, and audit-ready documentation, reducing the manual effort of preparing for regulatory deadlines.

Also working to NIST CSF 2.0? Read about NIST CSF 2.0 compliance, or run the free Self-Service Assessment for a NIS2 gap report.

Compliance that builds trust

Simplify compliance, mitigate risks, and build resilience with TENET.

FREE ASSESSMENTREQUEST DEMO

No credit card required. Connects to Azure and M365 in minutes. NIS2 coverage from day one.