
Who is NIST CSF 2.0 for?
NIST CSF 2.0 is a voluntary framework, not a legal mandate: built to apply regardless of size, sector, or maturity level
Even where it isn't mandated directly, CSF alignment is often the reference point these ask for
Built-in compliance intelligence
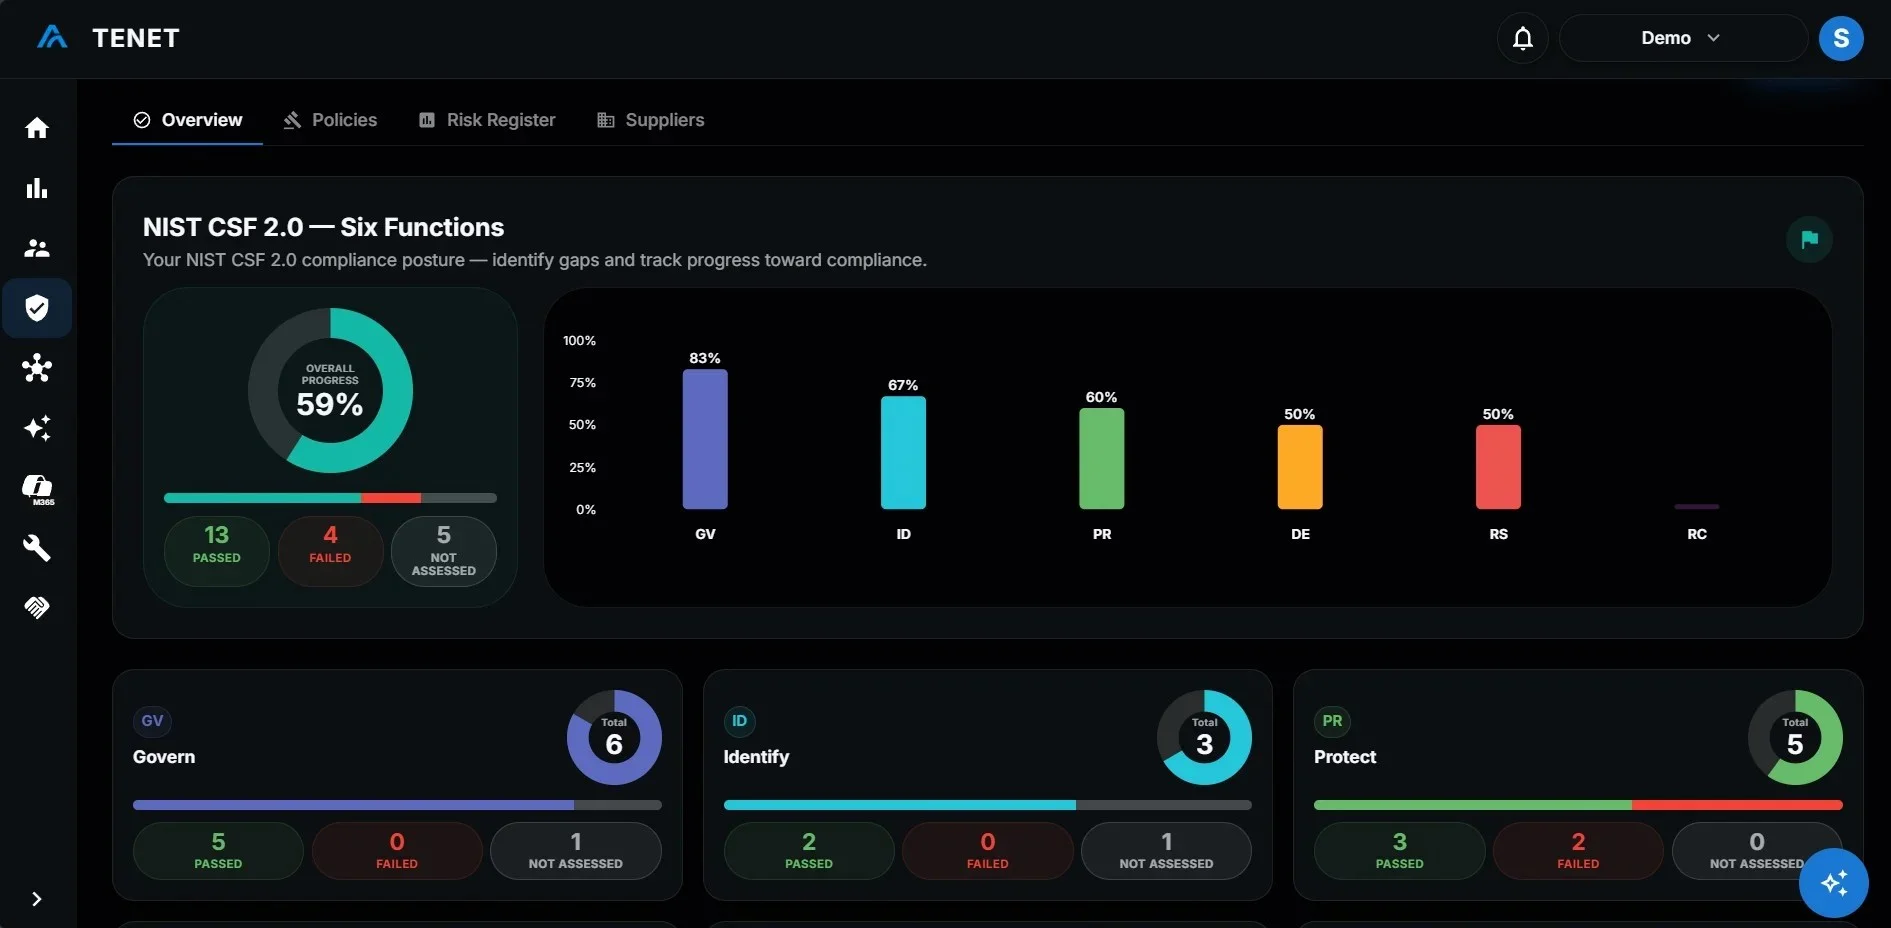
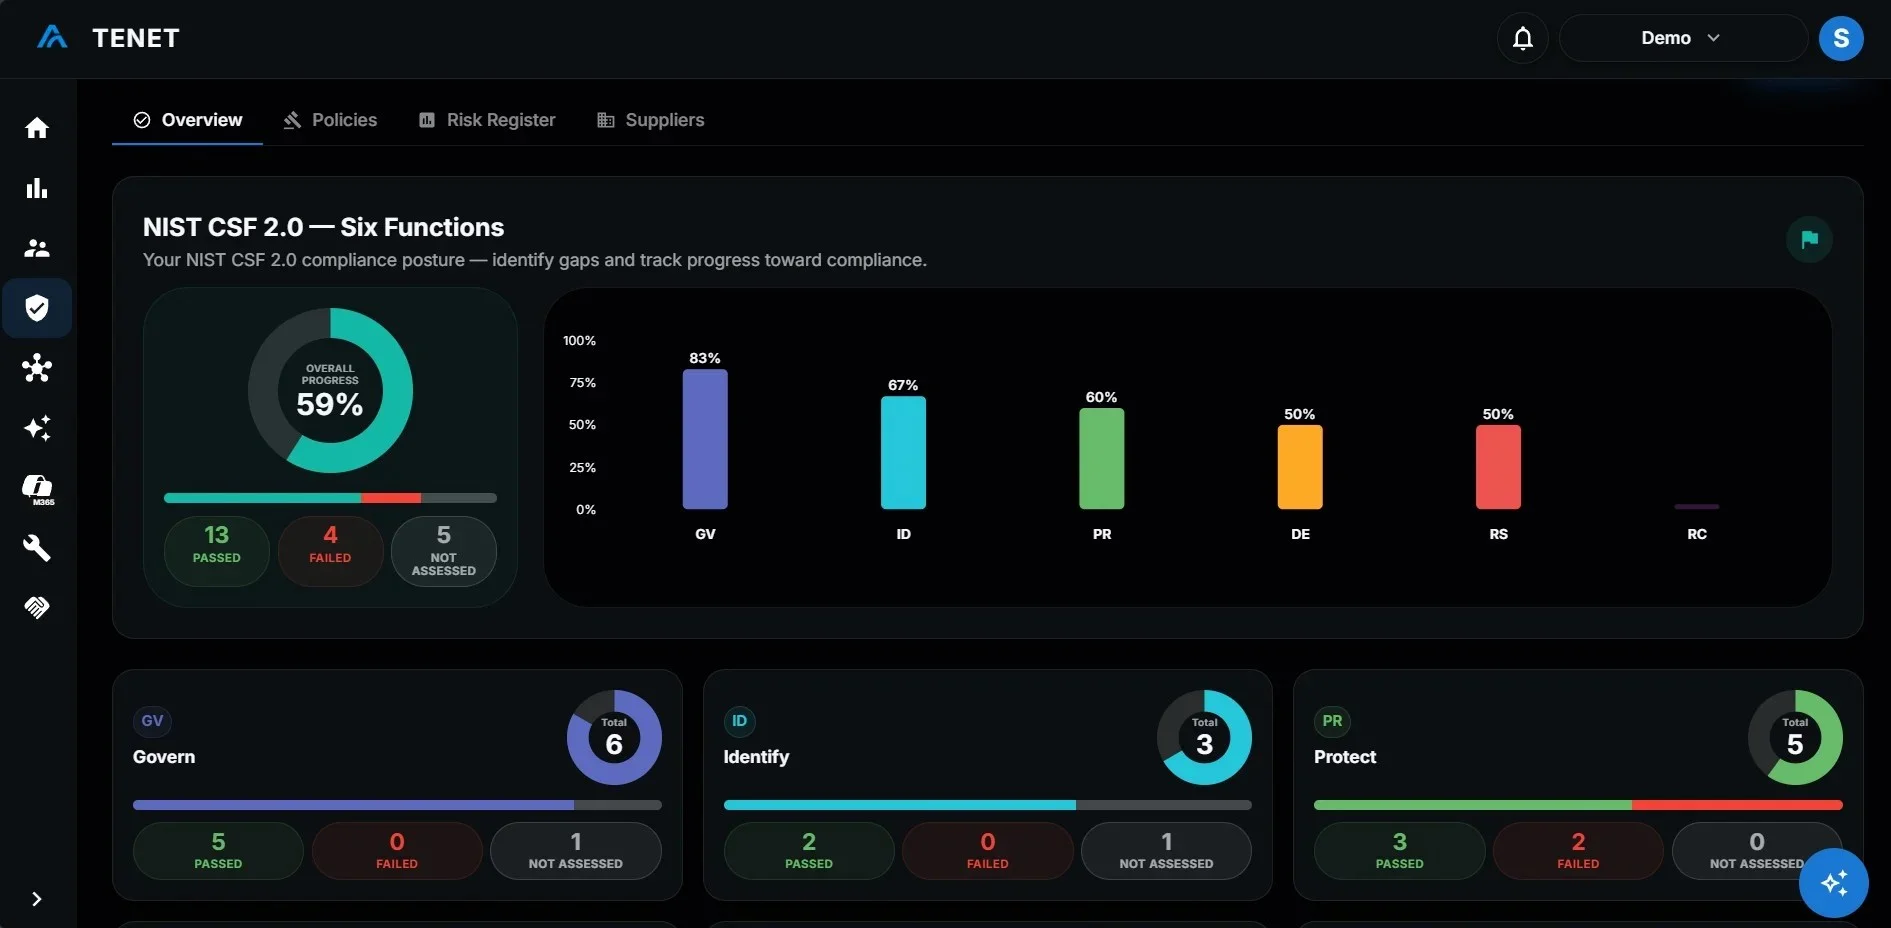
Detect compliance drift, generate reports, and monitor NIST CSF 2.0 posture through automated assessments across your Azure and Microsoft 365 environments.
Simplify investigation
Drill down from any of the six NIST CSF 2.0 functions into its categories, all the way down to controls and resource-level assessments across your Azure and Microsoft 365 environment. Questionnaires open with guidance on what good looks like from the NIST Implementation Examples, Microsoft 365 controls are grouped by Identity, Data, Apps and Device, and a toggle switches the same view to NIS2.
Compliance Drift Detection
Detect compliance drift on every refresh, not weeks later during a periodic review. TENET re-assesses your controls automatically so your posture stays current and audit-ready.
Risk-Based Prioritization
Surface the misconfigurations that carry the most compliance risk, ranked by control severity, so your team focuses remediation where it matters most.
What does NIST CSF 2.0 cover?
Benefits of NIST CSF 2.0
Reduce compliance friction
Automated scoring across all six NIST CSF 2.0 functions marks a requirement met when its mapped controls pass or its evidence is filed. Download the compliance report for auditors and focus remediation on the highest risks.
Catalog and manage business risk
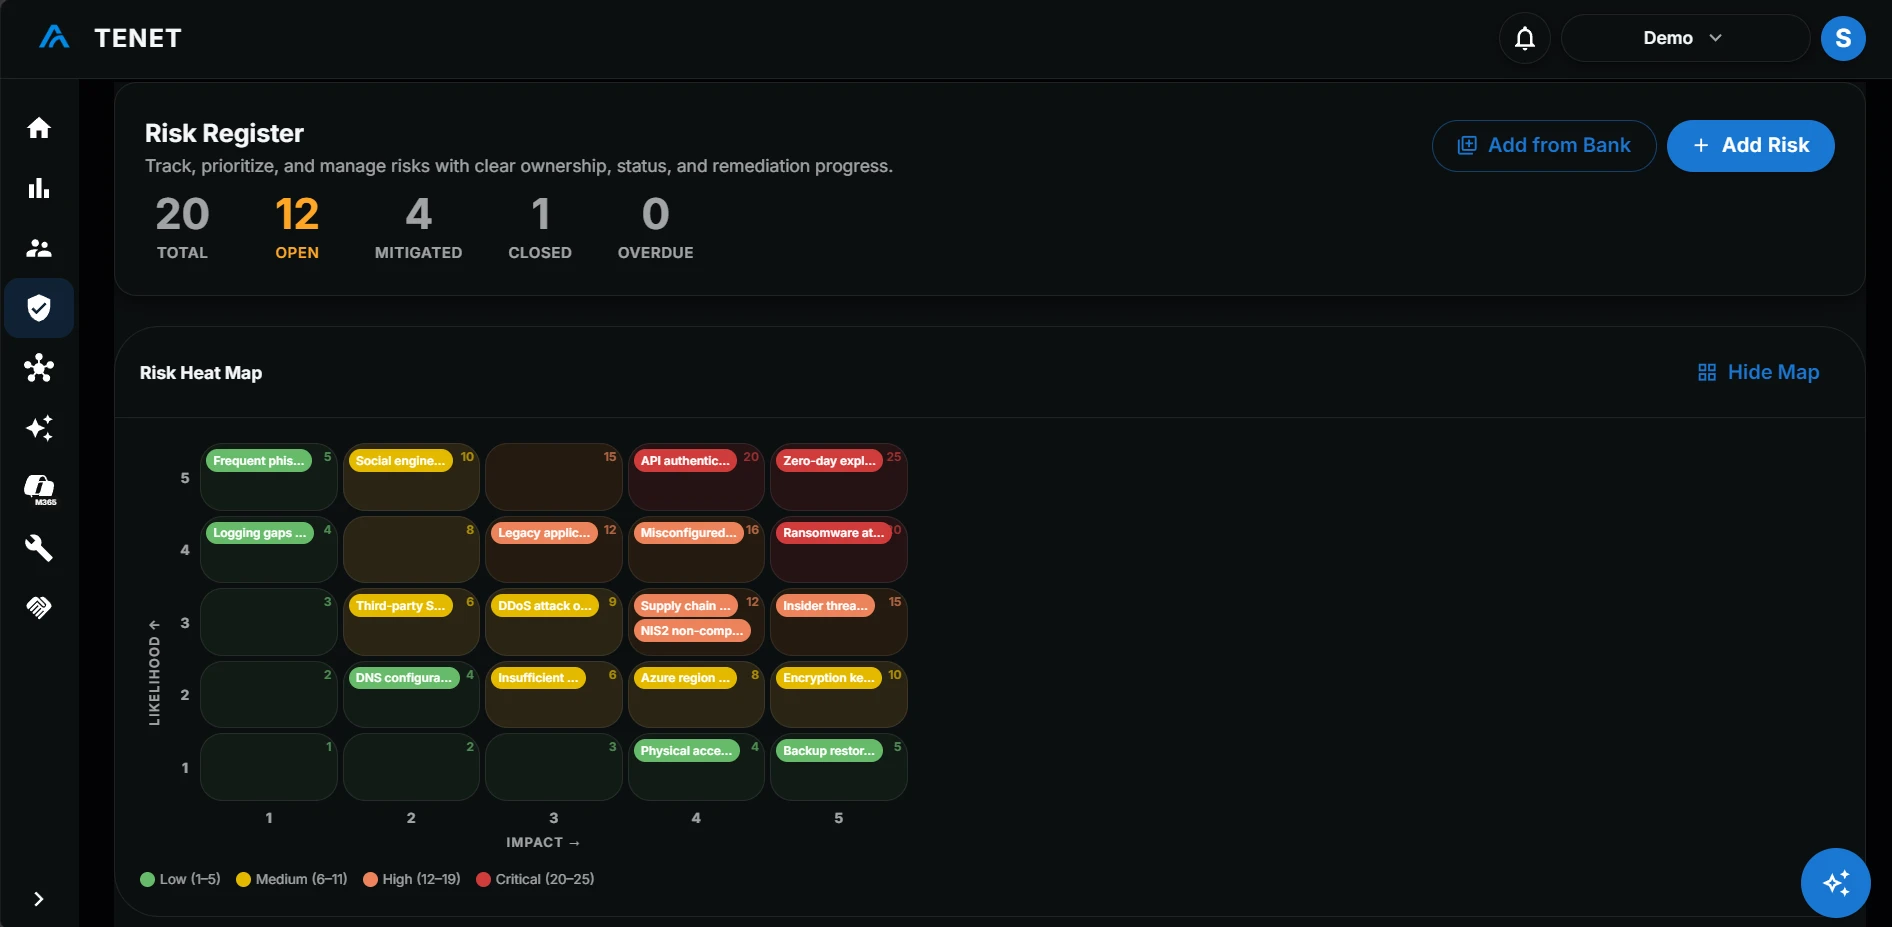
Create, catalog and visualize business risks in one place, starting from pre-built risk templates. Record clear assessment, ownership and treatment rationale to document your risk analysis for auditors.
LEARN MOREPolicy management
Store, version and manage your information security policies in one place, starting from ready-made templates. An active policy filed against a requirement counts as evidence toward it.
LEARN MORE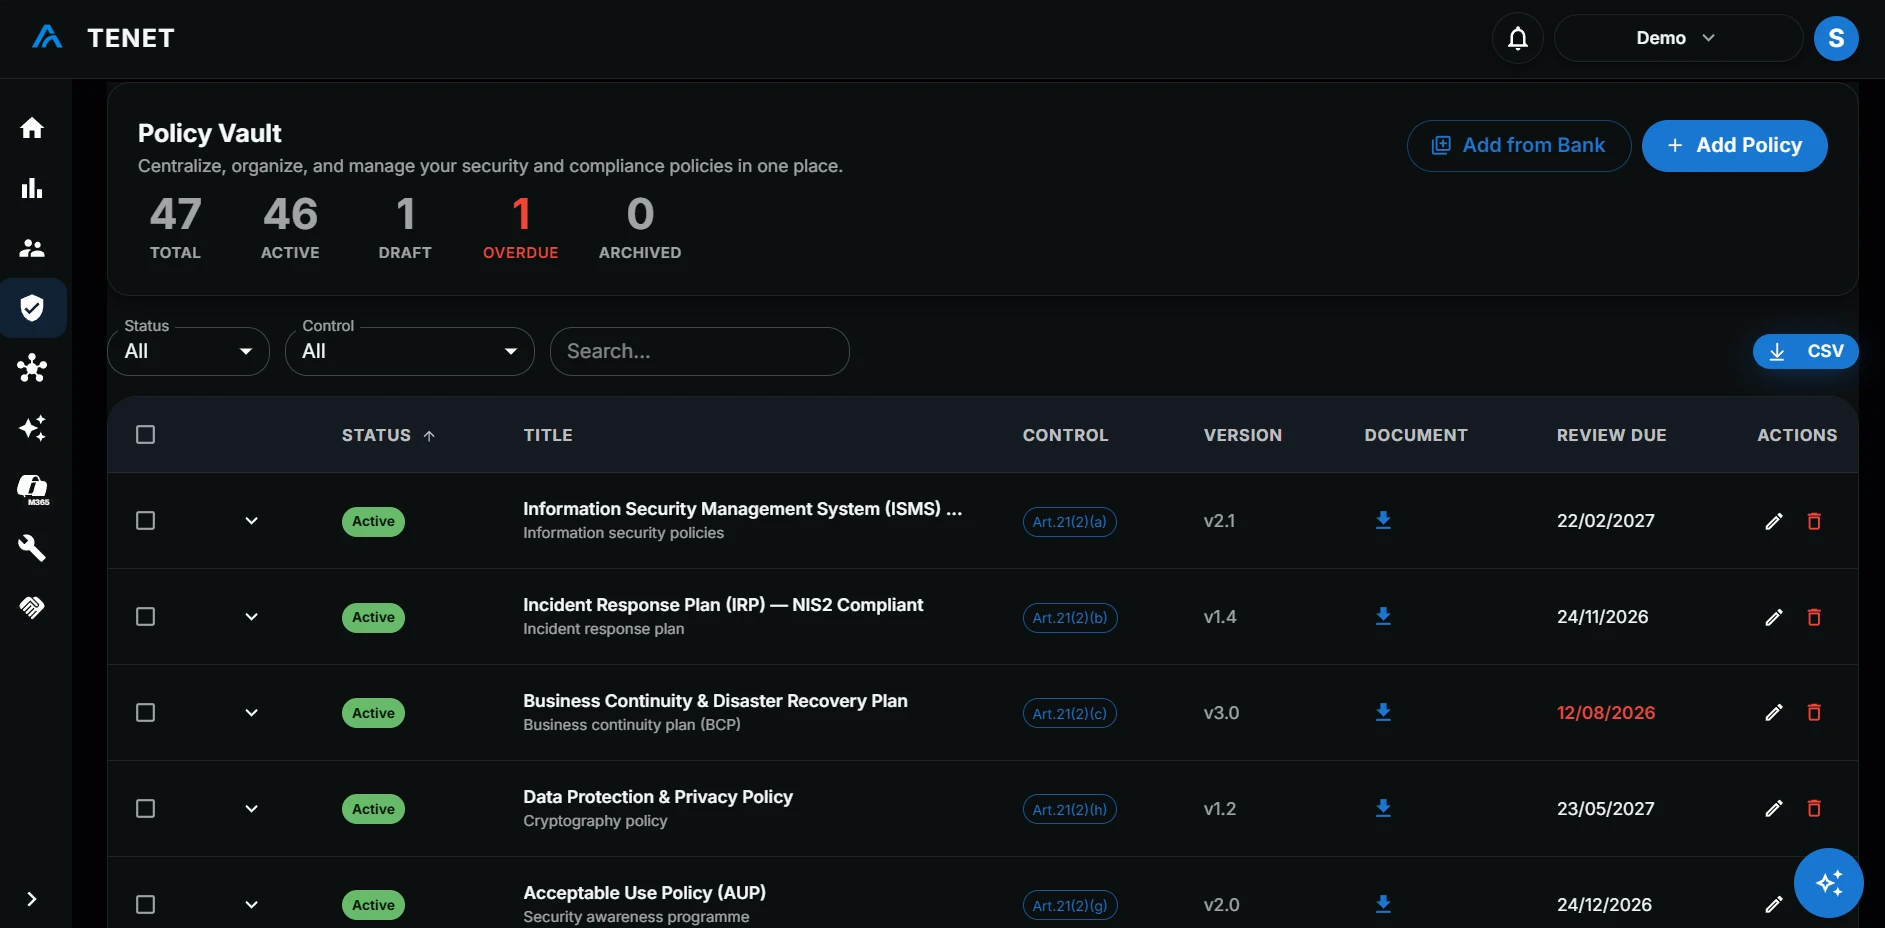
Integrated vendor risk management
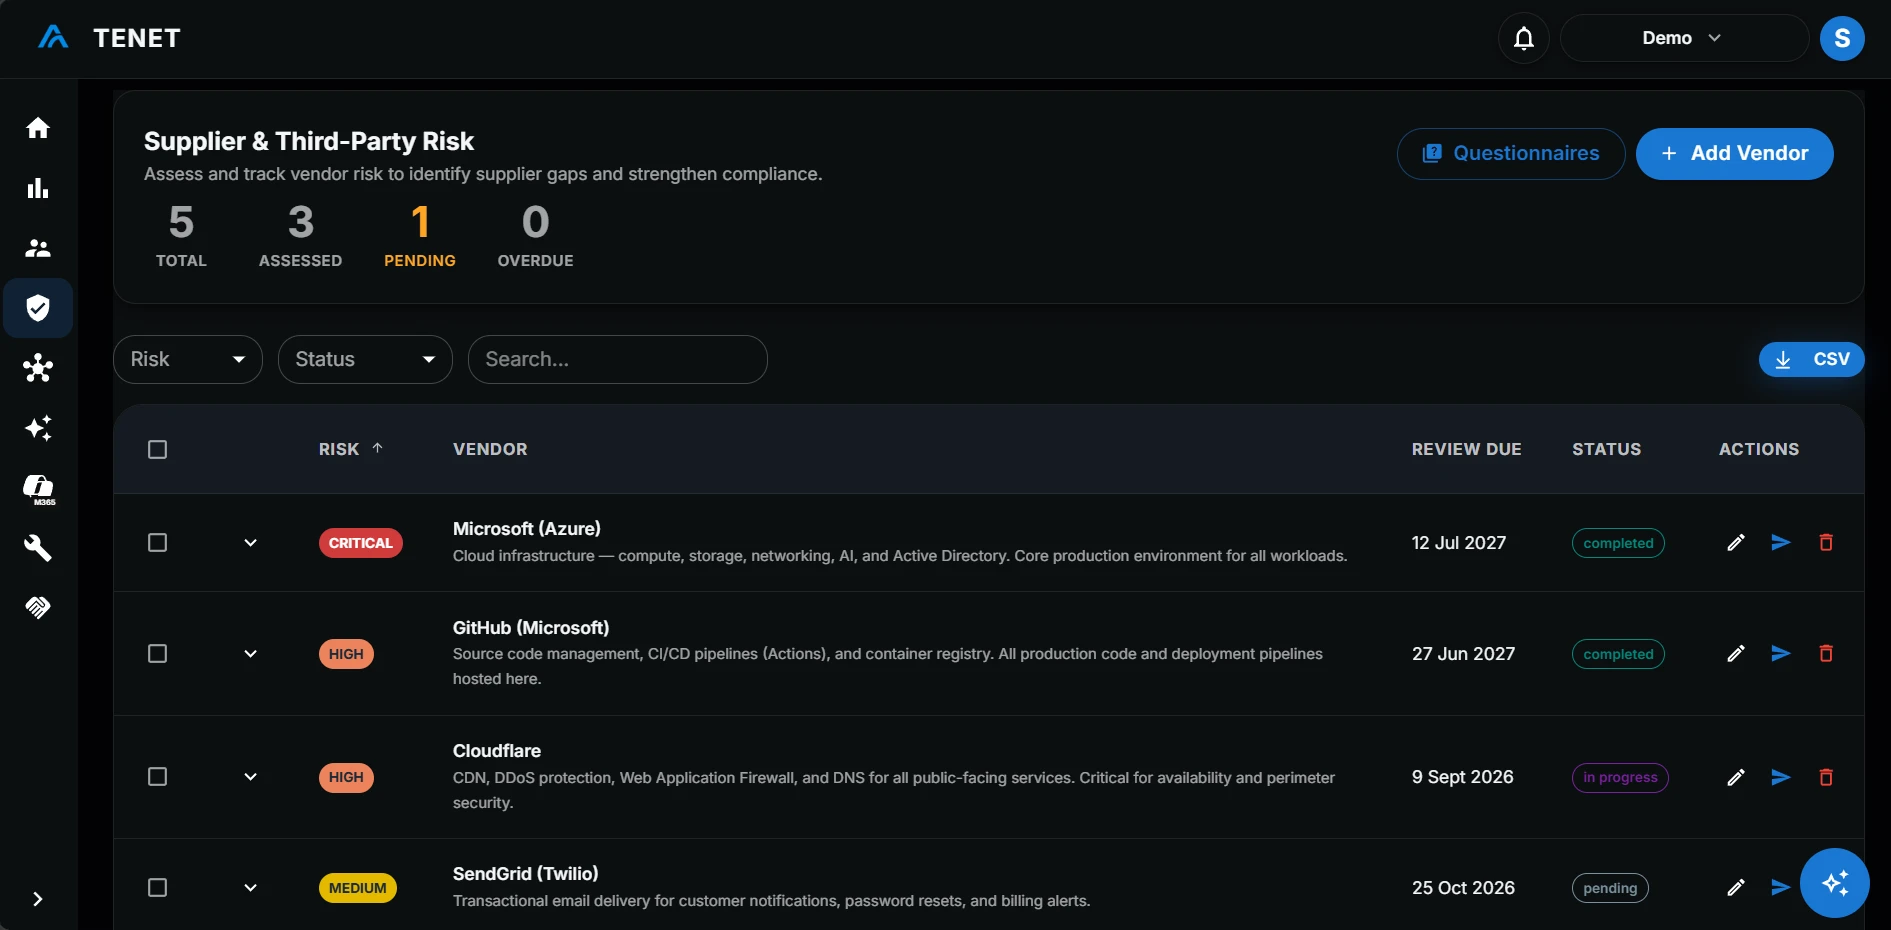
Supply chain risk sits in the Govern function of NIST CSF 2.0, and managing it manually quickly becomes unsustainable. Maintain your IT supplier inventory, integrate supply chain risk into your compliance posture, and use questionnaires.
LEARN MOREEvery compliance workflow in one place
Beyond framework dashboards, TENET ships a full suite of compliance modules that keep your program complete and audit-ready.
Respond and Recover Readiness
Cover the Respond and Recover categories, from incident management to recovery planning, with guided questionnaires and policy evidence.
Accelerated Remediation
Reduce mean time to remediation with a unified platform that enables teams to assign issues with remediation guidance to the right owners, and progress tracking until resolution without ever leaving the platform.
Exec-Ready Reports
Generate on-demand compliance reports that translate technical posture data into clear summaries your leadership and board can act on, in multiple languages and with no slide-deck assembly required.
Align with NIST CSF 2.0
TENET gives a clear, structured approach to NIST CSF 2.0, helping you strengthen operational resilience, manage cloud risk and demonstrate a mature security posture. Move from reactive controls to an always-current program.
Aligning with NIST CSF 2.0 is not just about implementing controls. It is about ensuring your organization can govern, identify, protect against, detect, respond to, and recover from cyber threats while maintaining critical services.
FAQs
What is NIST CSF 2.0?
Is NIST CSF 2.0 mandatory?
What are the six functions of NIST CSF 2.0?
How is NIST CSF 2.0 different from NIS2?
NIS2 is an EU legal directive with mandatory compliance obligations, defined in-scope sectors, incident reporting deadlines, and financial penalties for non-compliance. NIST CSF 2.0 is a voluntary, non-regulatory framework with global applicability and no built-in enforcement mechanism or fines. Many organizations use NIST CSF 2.0 as their internal risk management structure while separately tracking legal obligations like NIS2 for regulatory compliance.
Read more about NIS2 compliance in TENET.
How does TENET map to NIST CSF 2.0?
TENET automates the mapping of your security controls and evidence from Azure and Microsoft 365 to the NIST CSF 2.0 functions and categories. It provides continuously refreshed posture monitoring, automated reporting, and audit-ready documentation, reducing the manual effort involved in tracking alignment across all six functions.
Run the free Self-Service Assessment to get a NIST CSF 2.0 compliance report for your tenant.
Explore more resources
Compliance that builds trust
Simplify compliance, mitigate risks, and build resilience with TENET.
No credit card required. Connects to Azure and M365 in minutes.