Attack Surface Management

Attack Path Analysis

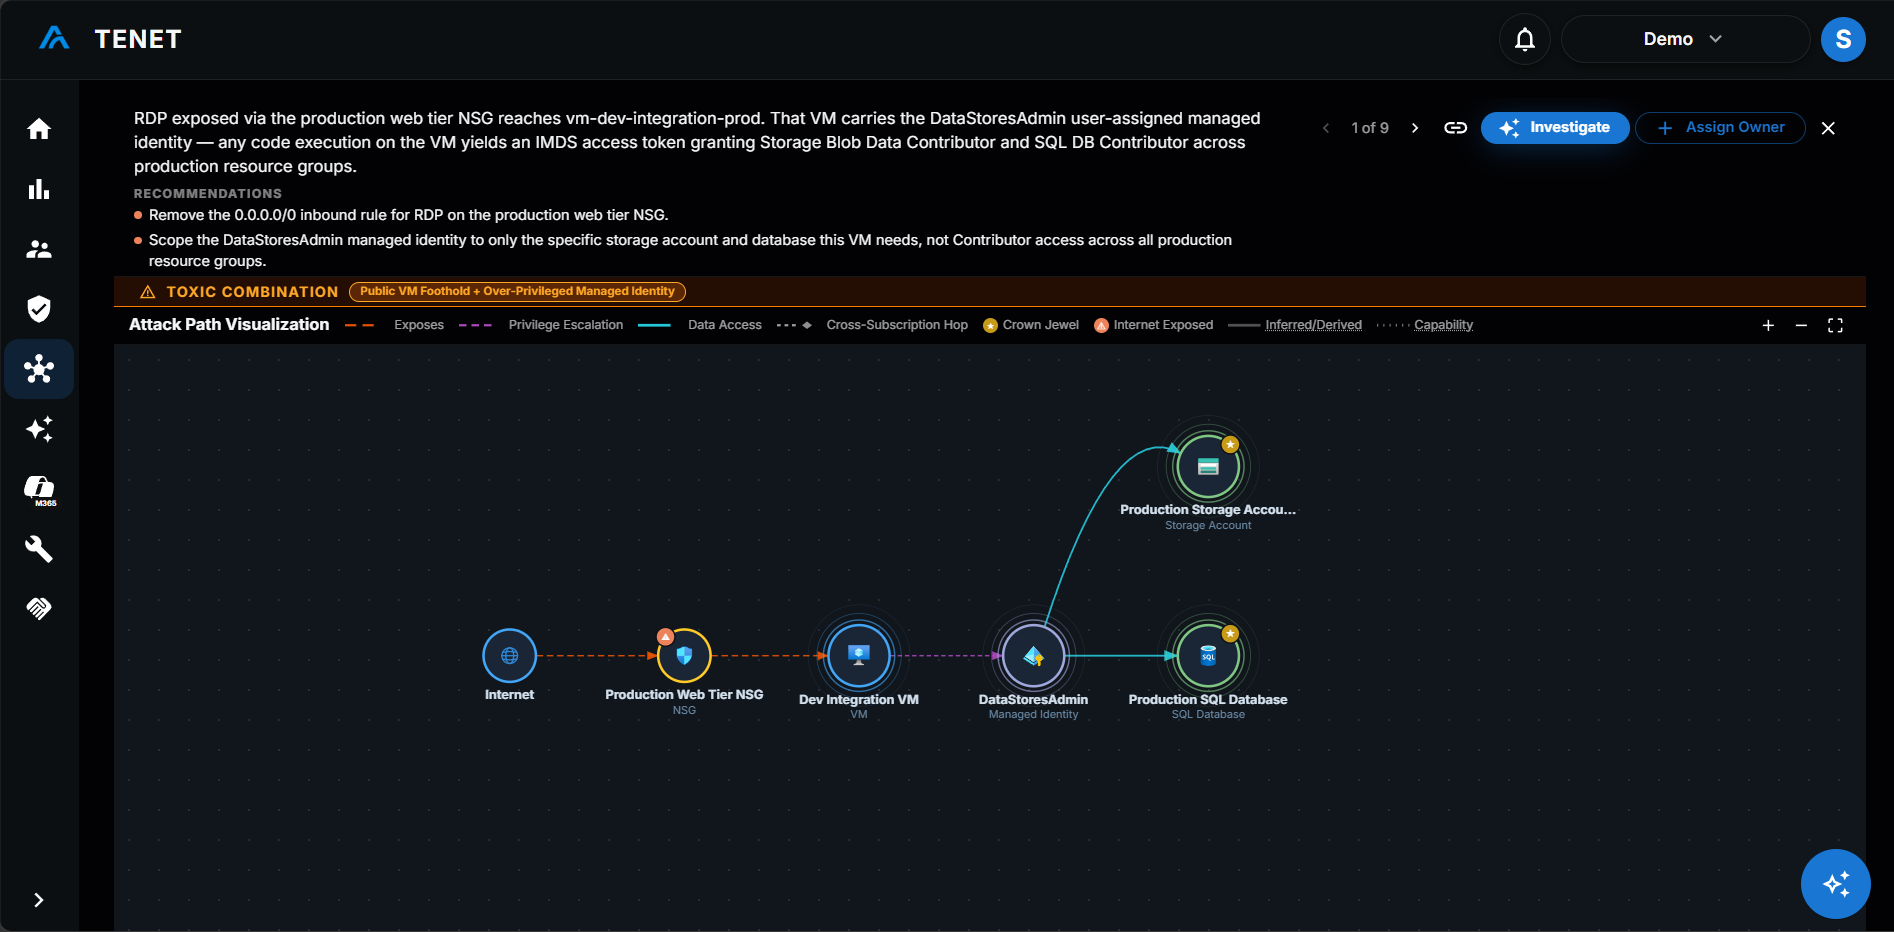
Trace the full chain from entry point to target across identities, subscriptions, resources, and Microsoft 365, not just a list of isolated findings.

START FOR FREEREQUEST DEMO
TENET attack path visualization from an exposed network security group through a VM and managed identity to production storage and a SQL database
Attack Path: End to EndCritical · 4 hops
hop 1hop 2hop 3Port10250Entry Pointaks-workloadWorkloadManagedIdentityPriv EscalationKeyVaultCrown JewelT1190T1078T1548T1555
Subscription: prod-coreIdentity abused: svc-aks-miImpact: Secrets exposure
Attack Path Analysis

Trace attacks to your crown jewels

You see the full chain from entry point to target, every hop, every identity abused, every subscription crossed. Not a list of misconfigured resources, but a traced route from initial exposure all the way to impact.

Toxic Combinations

Toxic risk combinations

A single misconfiguration is noise. Two that combine into a breach path are a real threat. TENET surfaces toxic combinations, such as an internet-exposed resource with a Contributor identity. Choke points show one fix closing several paths.

Toxic Combinations7 Active
①Internet-exposed resource
②Managed Identity with Contributor
Critical
→Control plane takeover pathvm-web-prod-01 + svc-mi-contrib
①High-anomaly service principal
②Elevated subscription role
Critical
→Credential abuse with lateral pivotsvc-deploy-sp + sub-prod-core
①OAuth app with Mail.ReadWrite
②Admin consent granted
High
→Mailbox data exfiltration pathxhr-sync-worker-v2
①Public storage blob
②Data store reachable
High
→Unauthenticated data exposurestorage-files-01 / exports/
Blast Radius: vm-web-prod-01
vm-webprod-01Entry Pointsvc-miVNetNSGKey Vaultsub-prodStorageAKS
47
Reachable Nodes
3
Max Hops
2
Hops to Crown Jewel
Blast Radius

Know the blast radius

Before you remediate, see how far an attacker could move from that entry point: reachable nodes, maximum hops, and the shortest path to the nearest crown jewel. Prioritize by blast radius, not by finding count.

MITRE ATT&CK

Place attackers in the kill chain

Attack paths are mapped to ATT&CK tactics and technique IDs wherever a path finding has a known technique. You see whether a path is Initial Access, Privilege Escalation or Lateral Movement, tied to your own resources.

MITRE ATT&CK: Path Breakdown
T1190Initial Access
Exploit Public-Facing Application
Port 10250 open on aks-nodepool-01
T1528Credential Access
Steal Application Access Token
aks-workload managed identity token
T1548Privilege Escalation
Abuse Elevation Control Mechanism
svc-aks-mi: Contributor on sub-prod-core
T1555Credential Access
Credentials from Password Stores
kv-prod-secrets: 14 secrets reachable
T1078Lateral Movement
Valid Accounts
Cross-subscription pivot via managed identity
Remediation Board3 Open
Block port 10250 on aks-nodepool-01In Progress
Entry node · 4-hop path to Key Vault · T1190 · Blast radius: 47 nodes
Security GraphPriority: CriticalOwner: a.patelDue: Today
Remove Contributor from svc-aks-mi on sub-prod-coreOpen
Pivot identity · used in 3 active paths · T1548 · Subscription: prod-core
Security GraphPriority: CriticalOwner: j.mooreDue: Today
Revoke Mail.ReadWrite from xhr-sync-worker-v2Open
Admin-consented · exfil path to storage · permission never observed in use
Toxic ComboPriority: HighOwner: s.chenDue: Tomorrow
Restrict public blob access on storage-files-01Completed
Data store · reachable from 2 attack paths
Toxic ComboPriority: HighOwner: a.patelDue: Apr 27
Remediation

From risk to remediation

Select any attack path to triage it on your Remediation board: assign an owner, set a due date, or open it in BriteAI. Each path shows a plain-language description, up to three ranked fixes and a first-seen date.

Azure & M365 Paths

Paths across Azure and Microsoft 365

The Security Graph extends into Microsoft 365, mapping paths from an OAuth-consented app through a mailbox or data sync into Azure. Admin-consented apps start from a signed-in tenant user, not the internet.

Cross-Surface Attack PathsAzure + M365
OAuth App (M365)→Mailbox access→Data Sync API→Azure Storage
Critical
4 hops·T1528T1114T1537
OAuth App (M365)→SharePoint files→Shared link exposure→Azure Blob
High
3 hops·T1528T1213T1530
OAuth App (M365)→Calendar access→Admin consent pivot→Key Vault
High
3 hops·T1528T1078T1555
Graph Node Types: Extended
Azure IdentityM365 IdentityMailboxSPO SiteOAuth AppAzure Storage
Threat Context: Defender for Endpoint + Microsoft Sentinel
Defender for Endpoint: Critical CVEs on Your Devices
CRITICAL
CVE-2024-21338
DESKTOP-ADMIN02 · Windows 11
CVSS 9.8
HIGH
CVE-2024-29988
LAPTOP-FIN07 · Windows 11
CVSS 8.8
HIGH
CVE-2023-44487
SRV-FILE01 · Windows Server
CVSS 7.5
Microsoft Sentinel Incidents
Credential Access: LSASS MemoryHigh
MITRE TA0006 · 3 correlated alerts
Threat Context

Bring threat context into the graph

Correlate findings across Azure and Microsoft 365 with Defender for Endpoint vulnerabilities and the incidents Microsoft has already raised, so the paths you prioritize carry real-world threat context, not just a theoretical score.

Incident Integration

Unified incident context

See Microsoft Sentinel and Microsoft 365 Defender incidents with unified cloud context. Use BriteAI to investigate root cause, and correlate incidents with the identities, workloads and attack paths in the Security Graph.

Incidents
1 Closed2 Active
Credential Access: LSASS MemoryHigh
MITRE TA0006 · 3 correlated alerts
SentinelAzure
Impossible Travel: admin@contoso.comCritical
MITRE T1078 · Entra ID Protection · 1 correlated alert
IdentityM365
Malicious OAuth Consent: DataSync ProHigh
MITRE T1528 · Closed · 2 correlated alerts
SentinelM365

See risk as an attacker would

Stop responding to alerts. Start closing paths. One graph connects identities, workloads, and data stores across your Microsoft cloud environment, so the threats worth fixing stand out.

FREE ASSESSMENTREQUEST DEMO